Tech Notes
Notes on tech, programming, and DevSecOps for the modern developer
Latest Posts
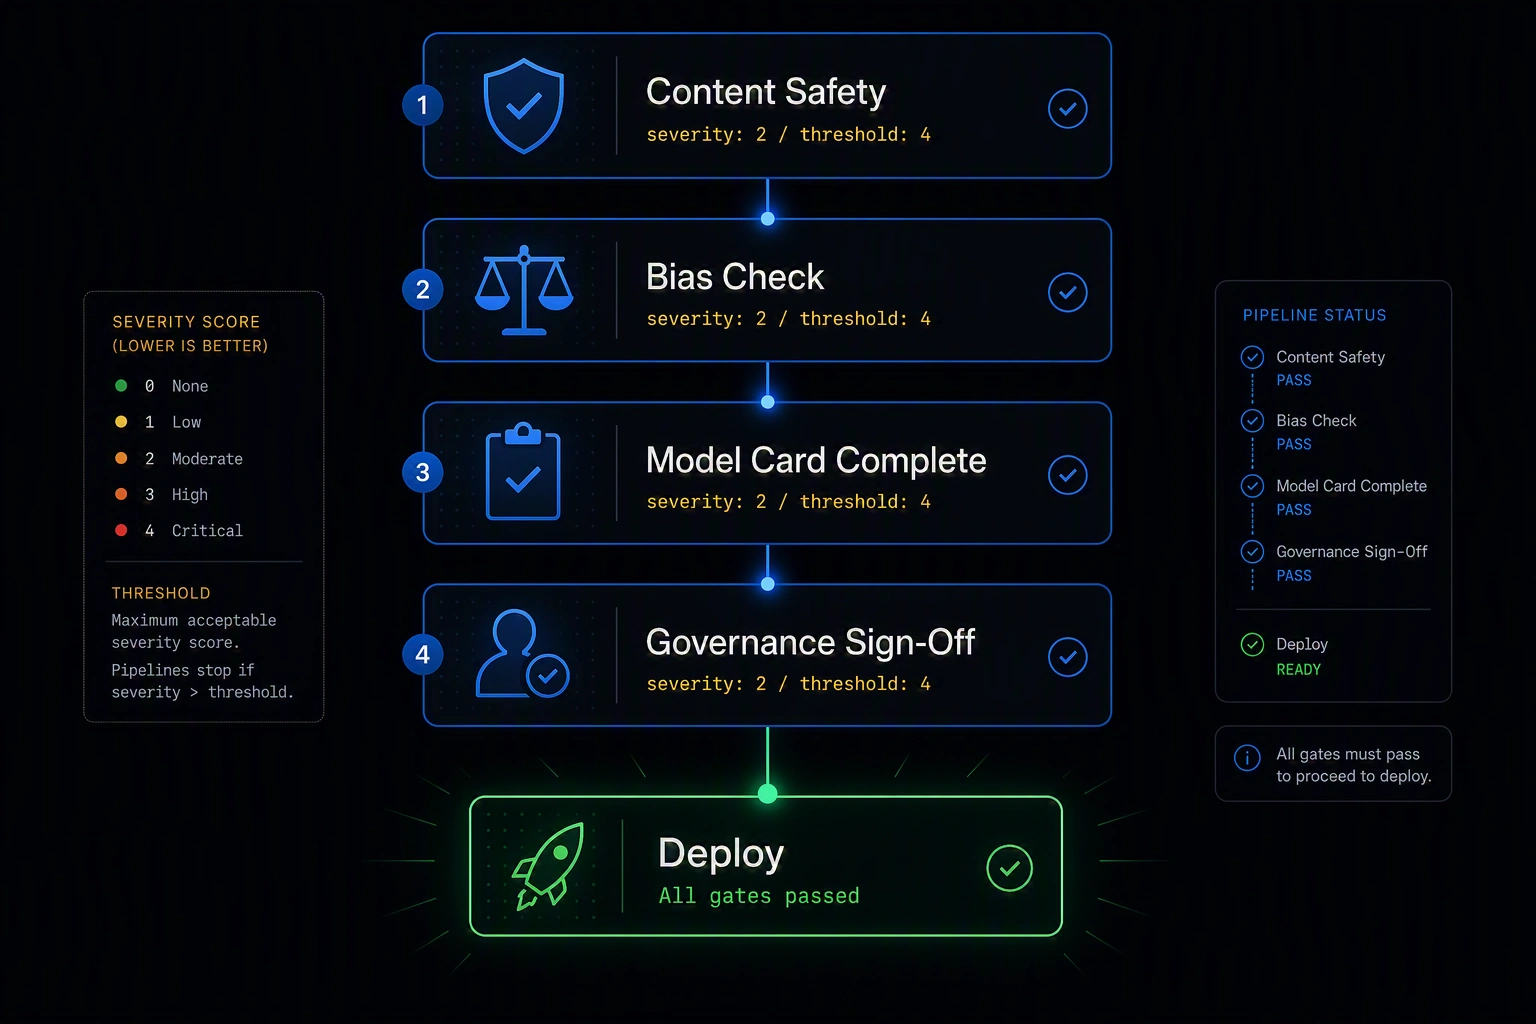
Responsible AI in the SDLC: Governance Gates You Can Automate with GitHub Actions
Responsible AI principles as a policy document nobody checks against shipped behavior isn't governance, it's a slide deck. This post maps three of Microsoft's Responsible AI principles to concrete, automatable GitHub Actions checks: content safety filtering with Azure AI Content Safety, bias detection via paired-prompt counterfactual testing, and documentation completeness enforced as a CI-validated model card - wired into a single deployment workflow gated by a GitHub Environments sign-off, plus an honest accounting of what this approach doesn't automate.
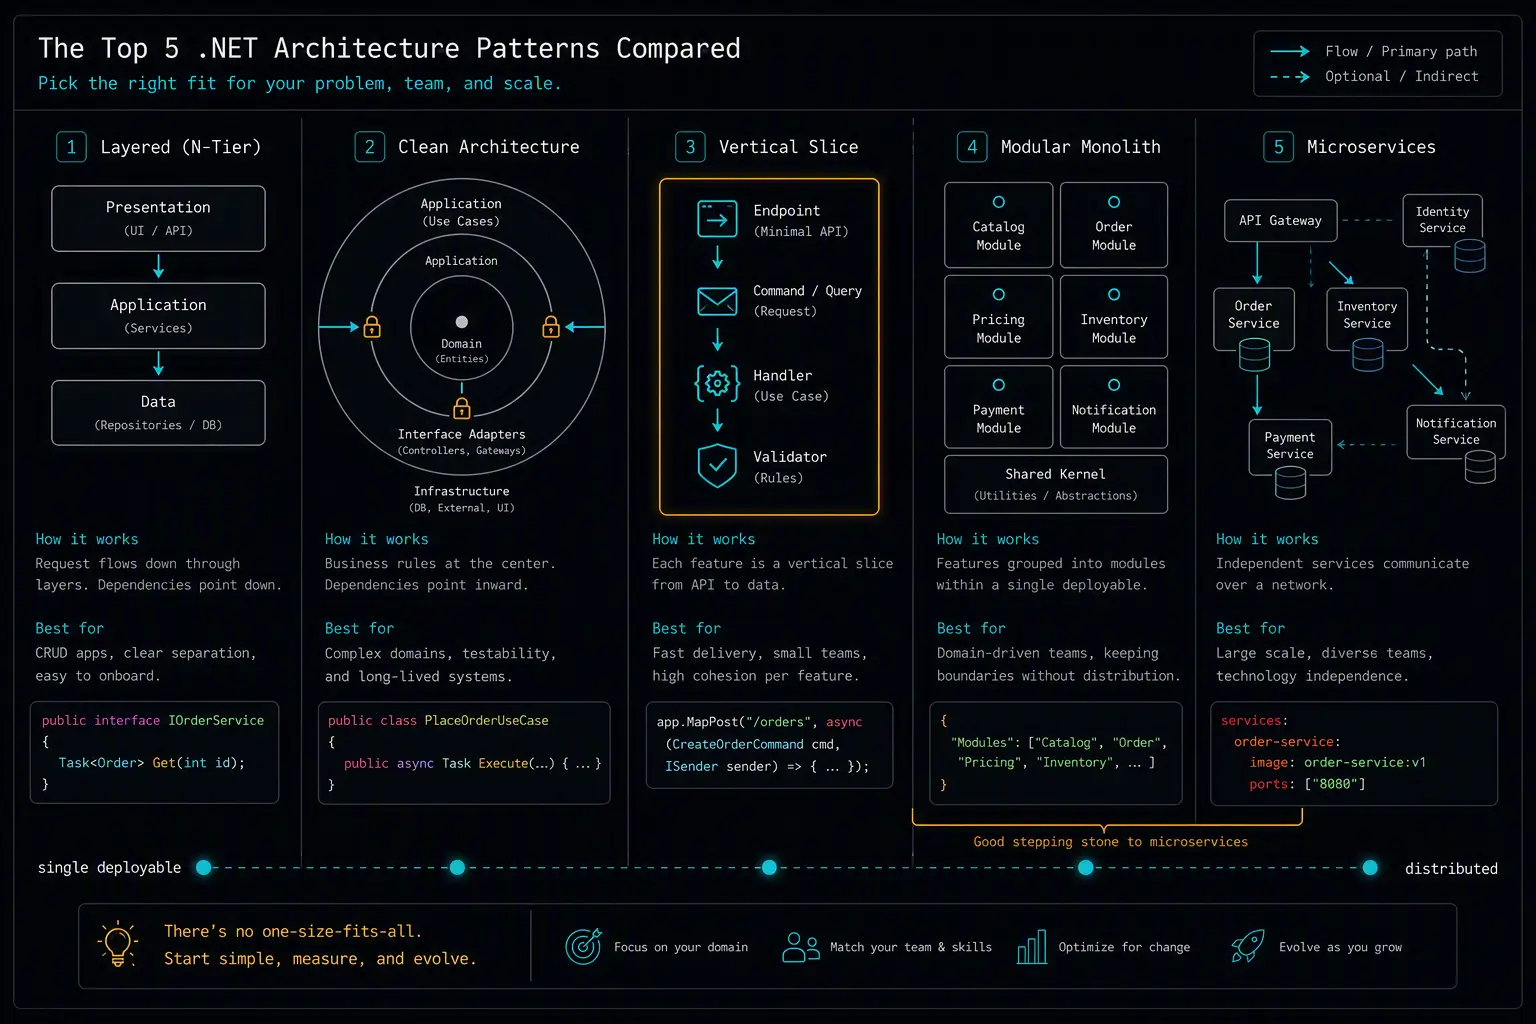
The Top 5 .NET Architecture Patterns Compared: Which One Should You Choose?
Layered, Clean, Vertical Slice, Modular Monolith, and Microservices all answer the same question differently. A practical breakdown of what each actually optimizes for, and which project profile fits.
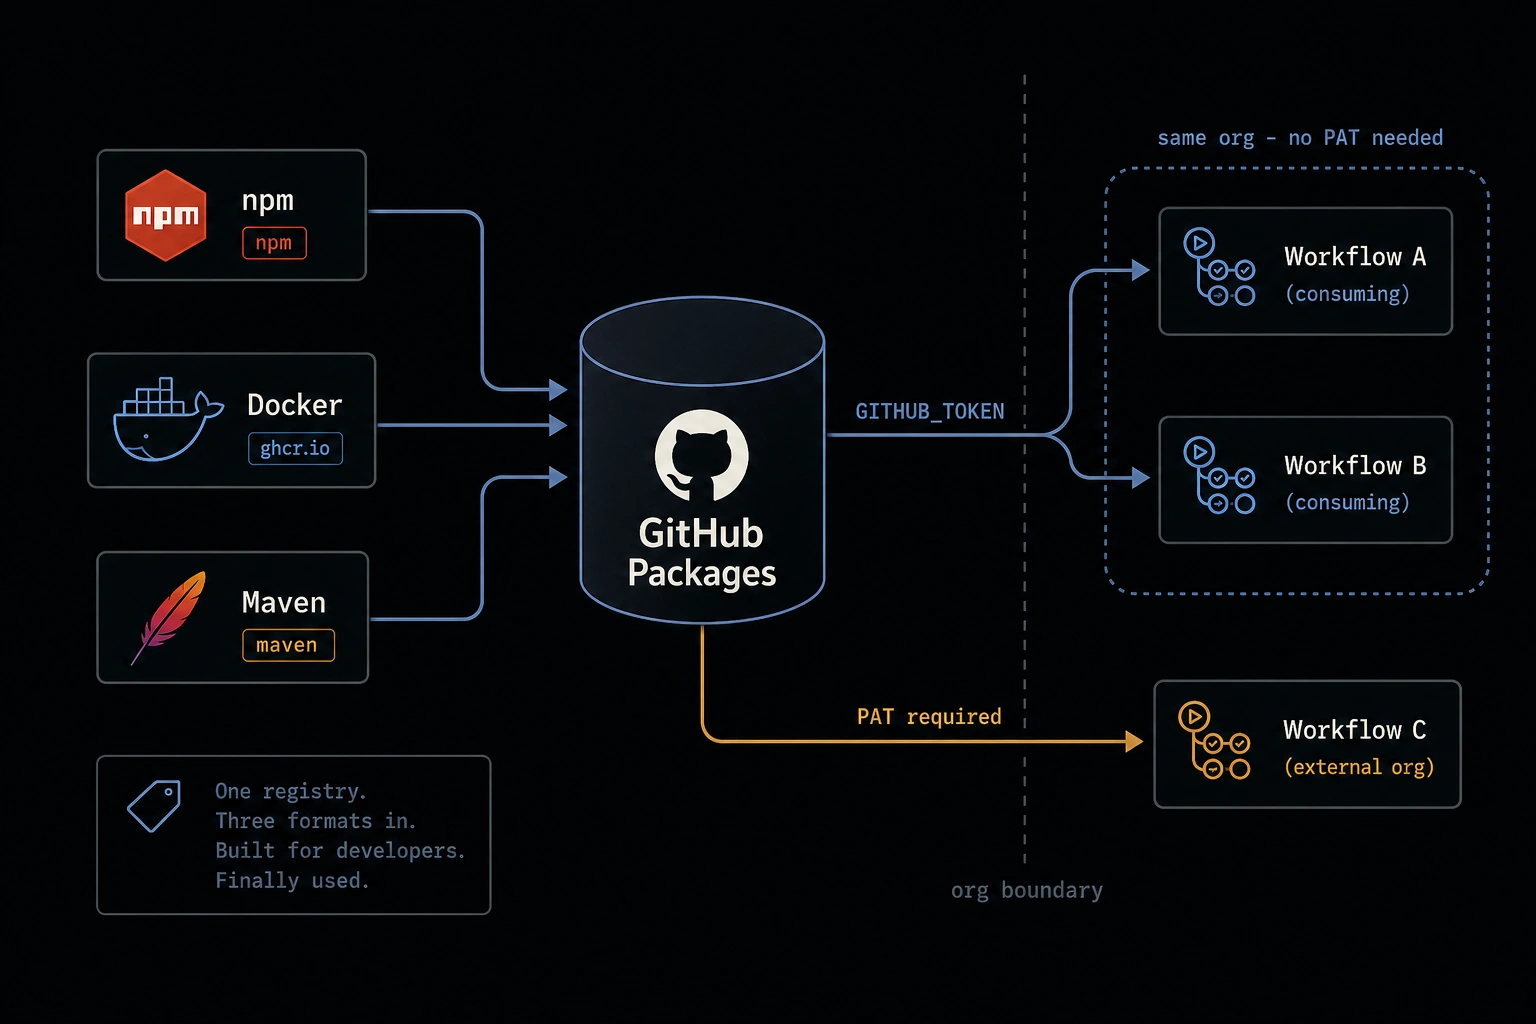
GitHub Packages as an Internal Registry: Publishing and Consuming npm, Docker, and Maven Artifacts
Most teams reach for JFrog, Nexus, or a public registry for artifact management without realizing GitHub Packages already does the job, tied to infrastructure they're already running and paying for. This post covers publishing npm packages, Docker images, and Maven artifacts to GitHub Packages from a GitHub Actions workflow, consuming them in downstream workflows using GITHUB_TOKEN with no PAT required for same-org access, setting package visibility and retention/cleanup policies, and the one real limitation: cross-org consumption needs a PAT after all.
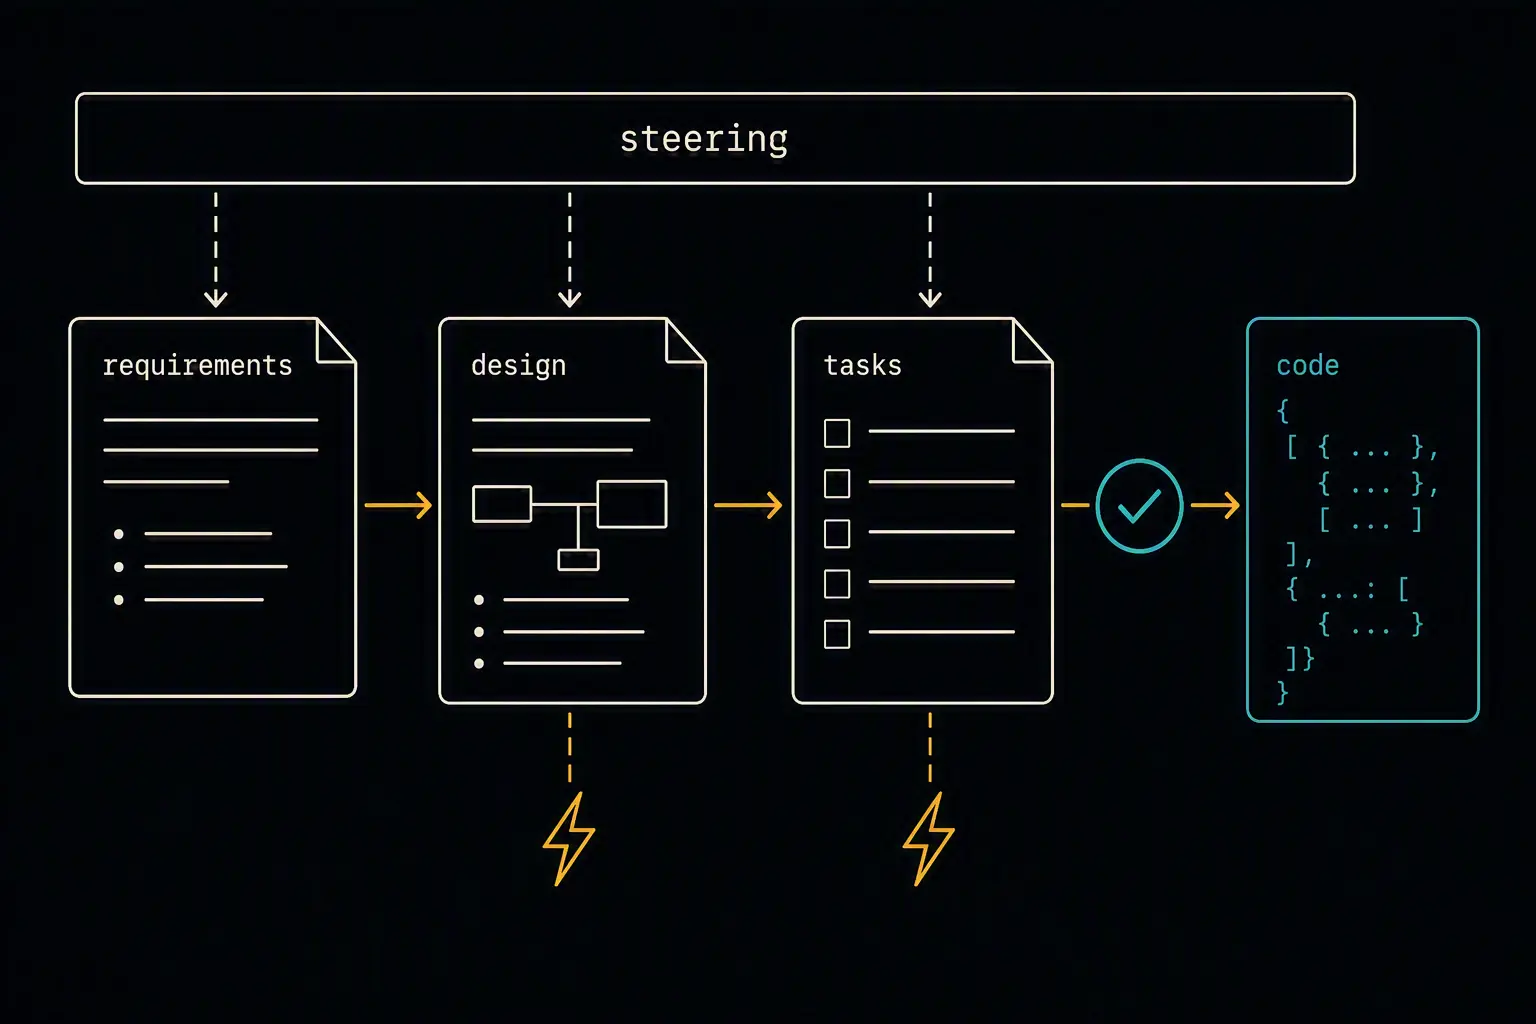
Getting Started with Kiro: Setup, Environment, and Best Practices
Kiro makes you write the spec before the code. A setup guide for steering docs, specs, and hooks - and an honest look at when that upfront cost pays off.
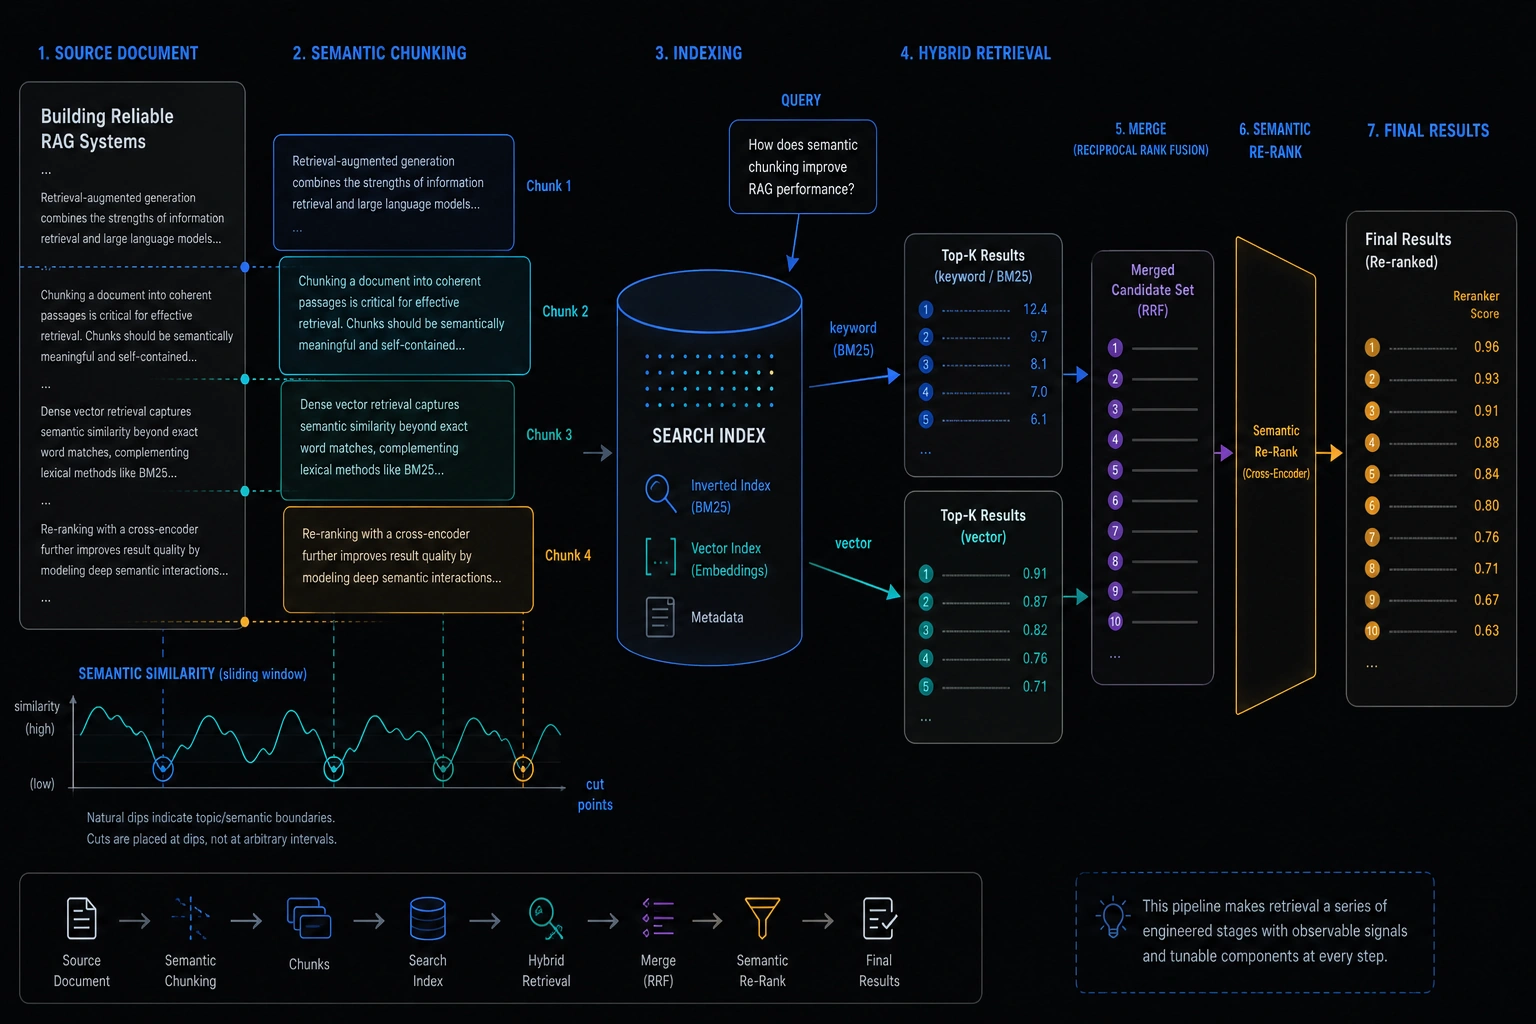
RAG in Production: Chunking, Indexing, and Observability with Azure AI Search
A RAG prototype is a similarity search and a prompt template - production RAG is the accumulation of decisions made before generation ever runs: chunking strategy, index schema, hybrid search versus vector-only, and whether you re-rank. This post covers fixed-size versus sentence-boundary versus semantic chunking, building an Azure AI Search index with vector and semantic configurations, hybrid search with reciprocal rank fusion and the semantic ranker, a recall@k metric to evaluate retrieval independently of generation, and an Azure AI Foundry groundedness evaluation run scored against retrieved context.
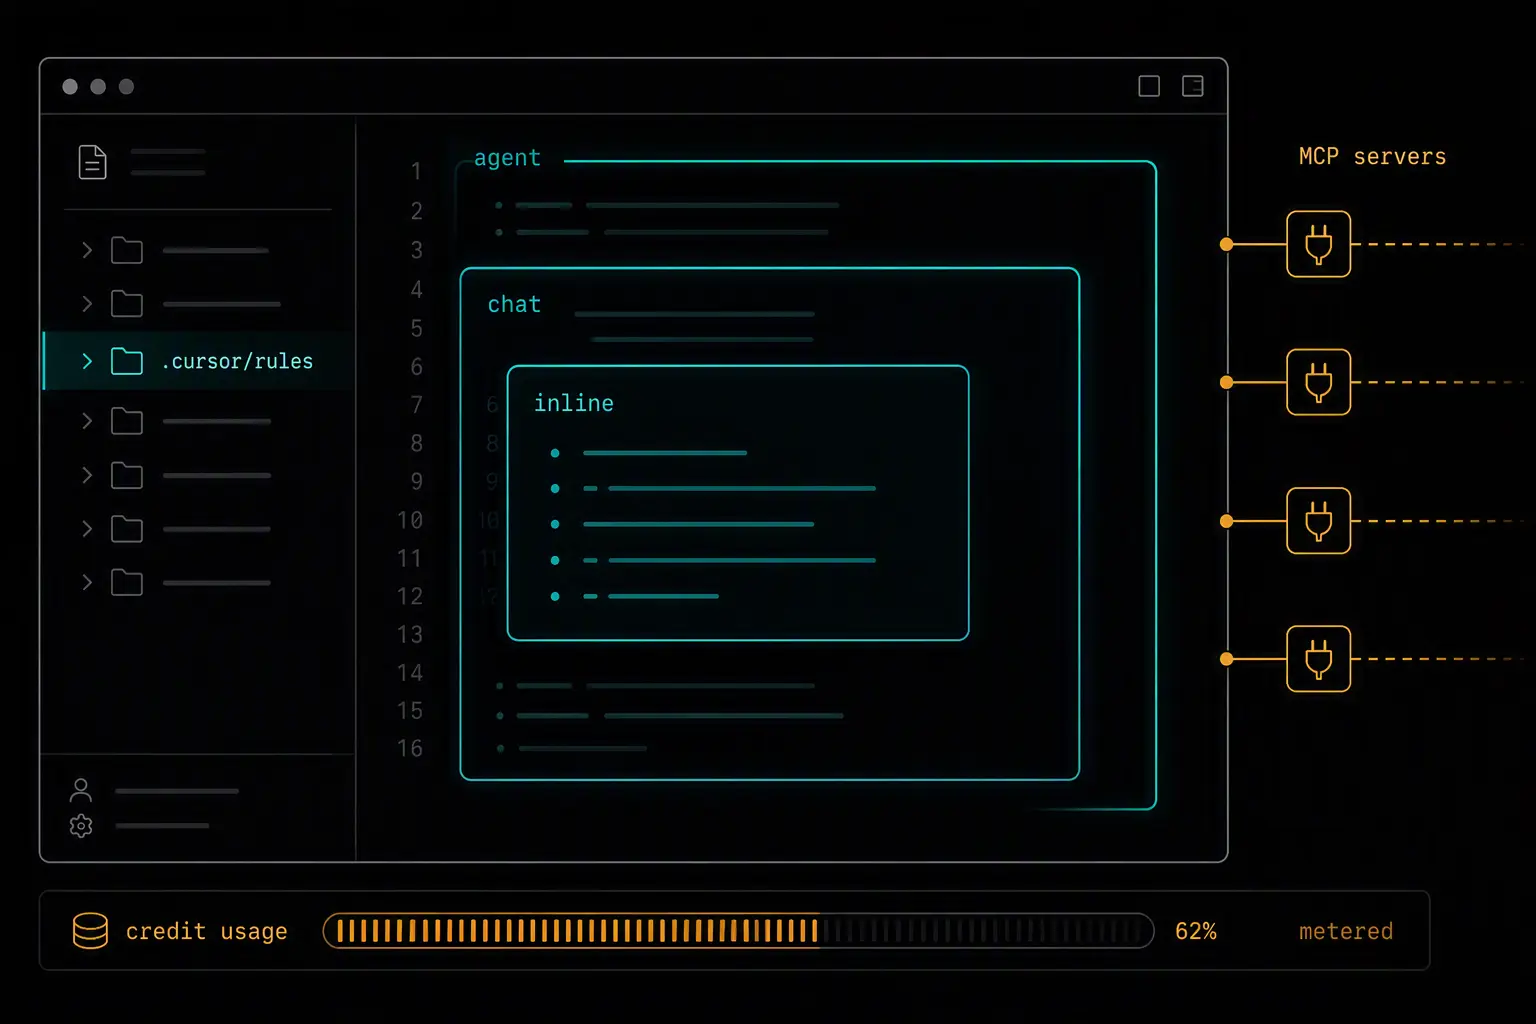
Getting Started with Cursor: Setup, Environment, and Best Practices
Cursor feels like VS Code until you open .cursor/rules/ and MCP config. A setup guide for scoped rules, the three AI surfaces, and keeping credits in check.
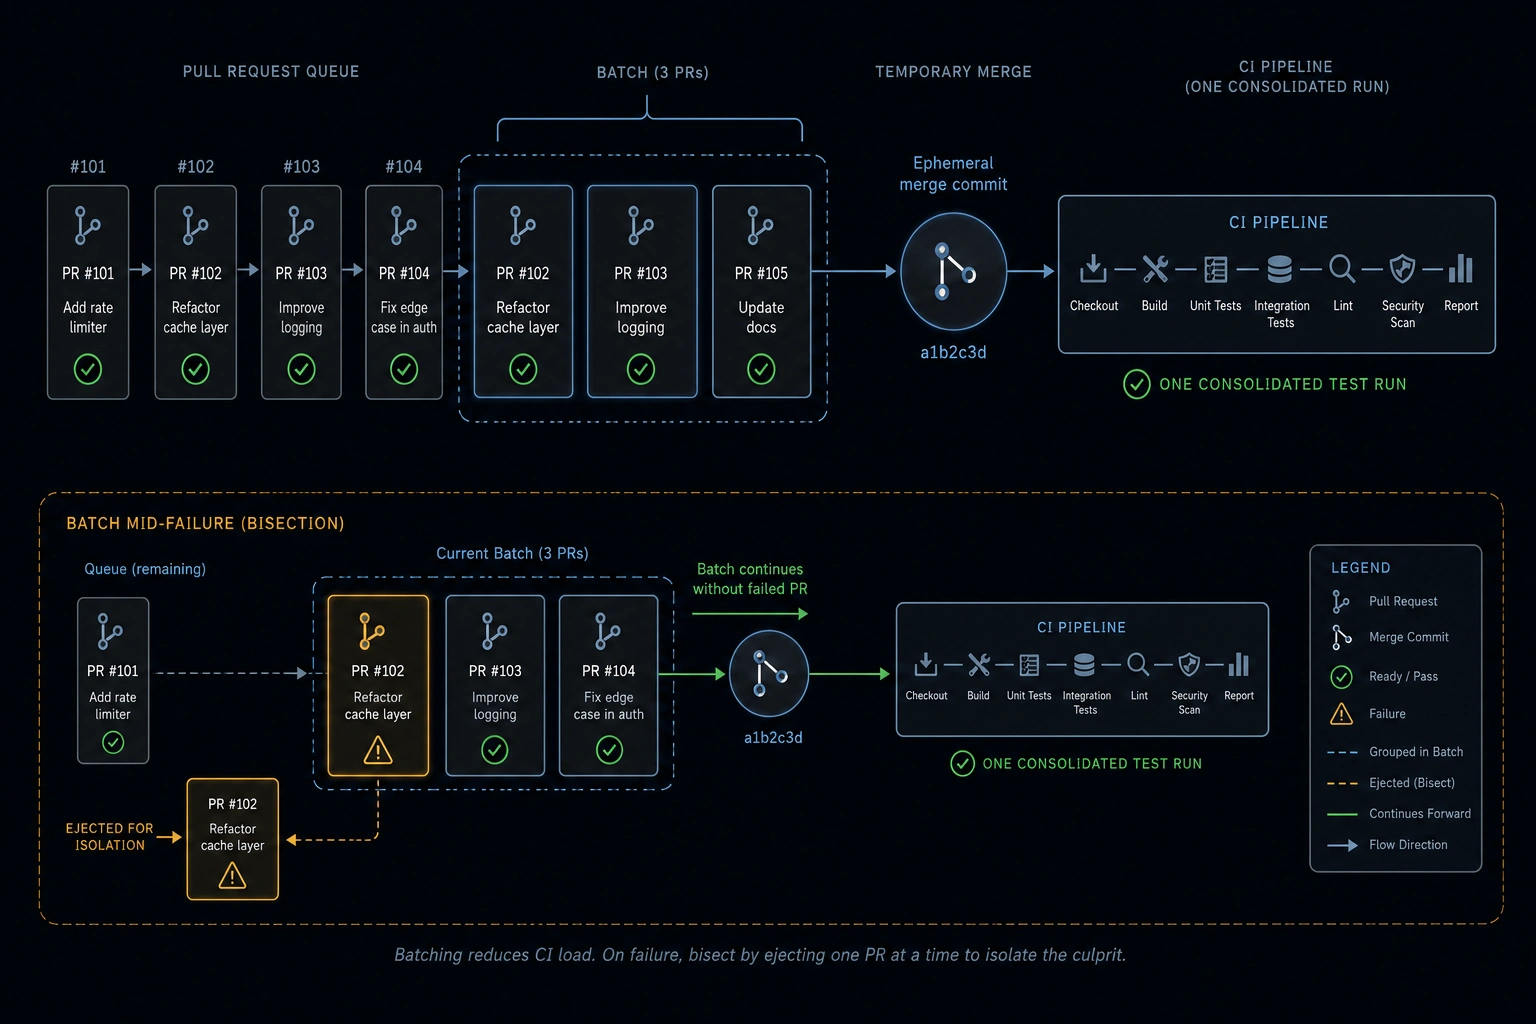
GitHub Merge Queues: Safe, Scalable Merging Without Branch Protection Bottlenecks
Required status checks with a strict up-to-date policy don't scale: every merge invalidates every other open PR's status, forcing a re-run, which produces a queue where PRs re-validate against a constantly moving target. Merge queues fix this by batching. This post covers how GitHub's merge queue actually works, how to configure one through Rulesets, the merge_group Actions trigger teams forget to wire up, what happens when a batch fails, and how the whole model traces back to bors and homu.
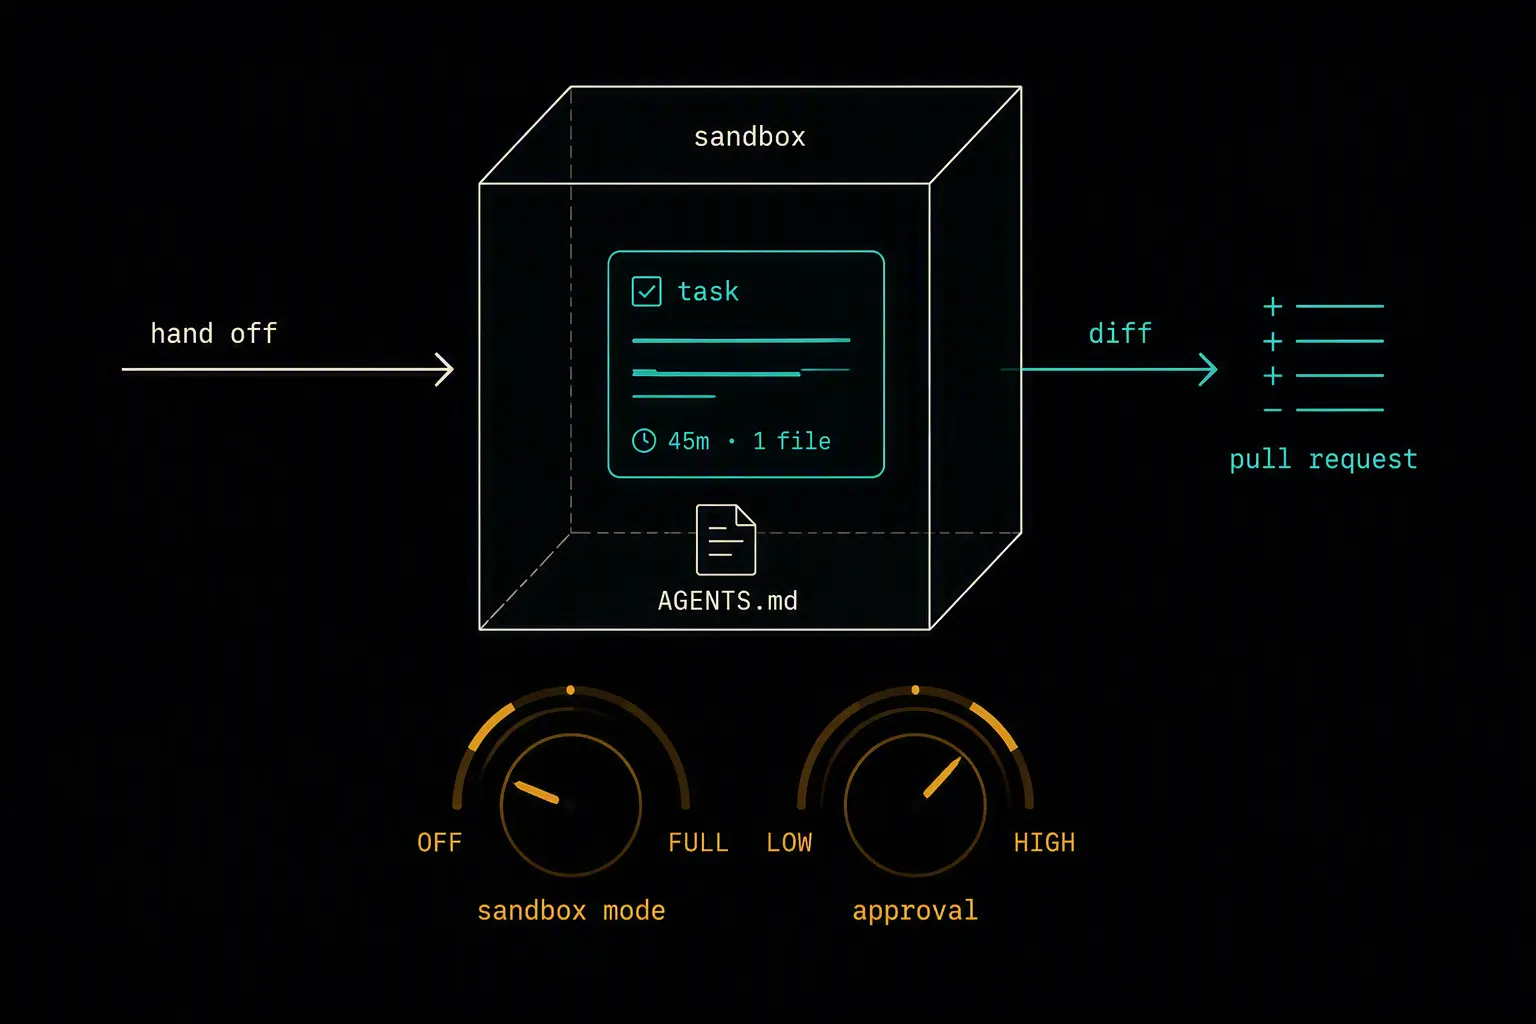
Getting Started with OpenAI Codex: Setup, Environment, and Best Practices
Codex assumes you'll hand off a task and walk away. Getting that right means AGENTS.md, sandbox mode, and approval policy - not just installing the CLI.
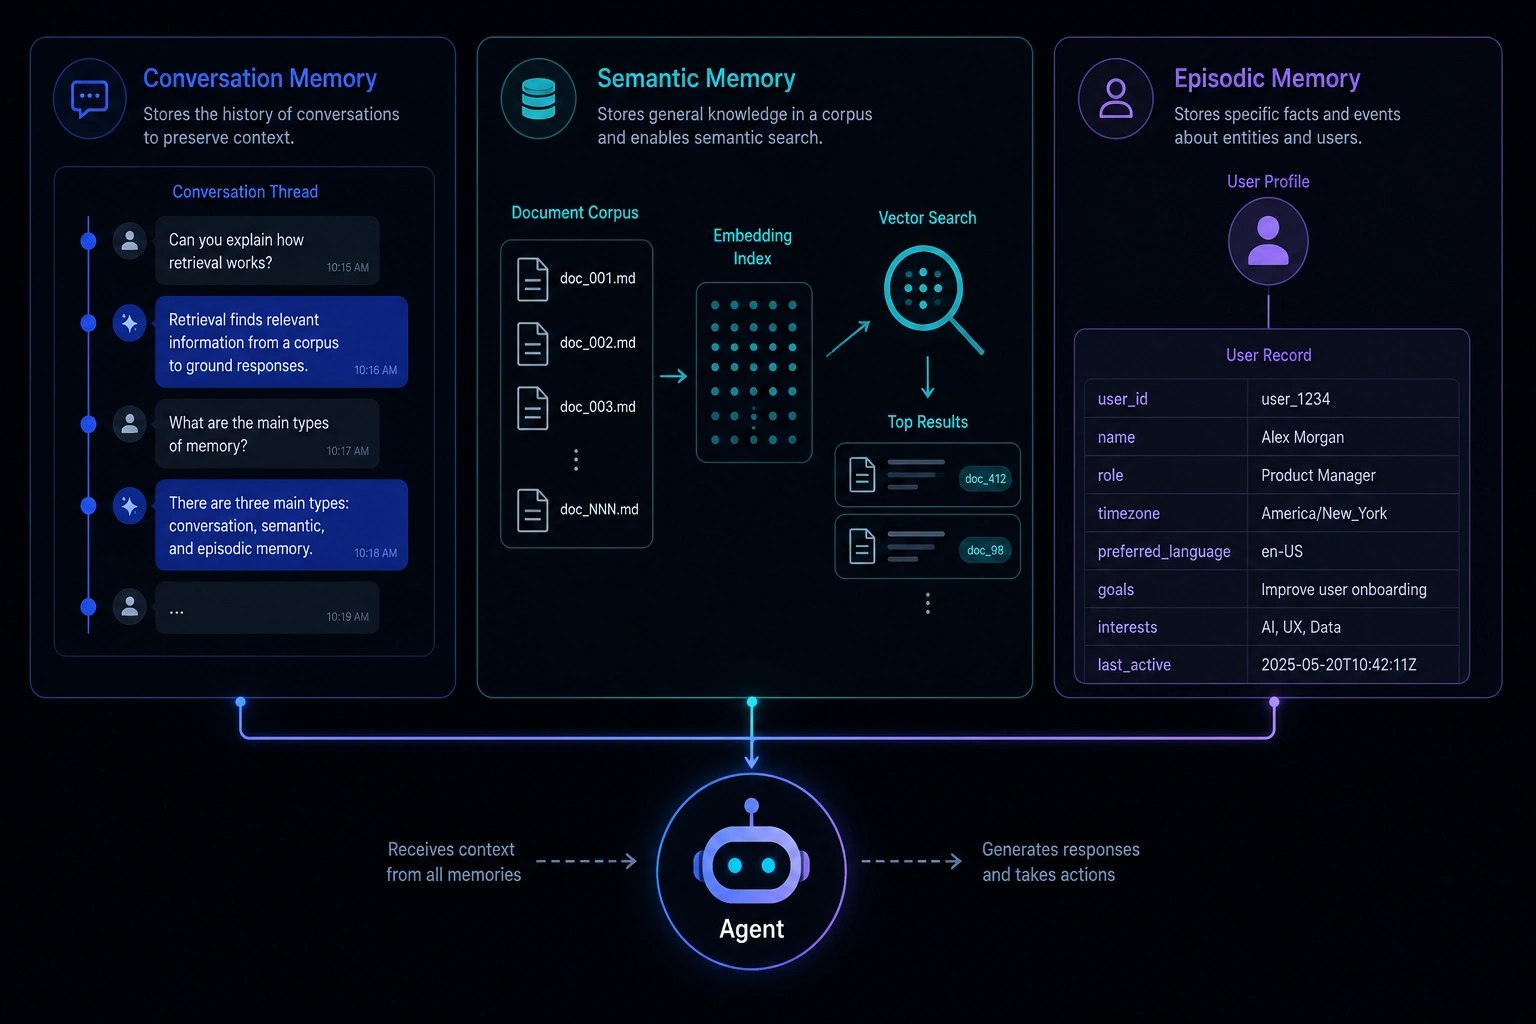
Azure AI Foundry Agents: Memory, Tool Calling, and Retrieval-Augmented Generation
Memory is what separates a useful agent from a stateless chatbot, but 'give the agent memory' is not one problem - it's three. This post covers the Azure AI Foundry primitives for conversation memory (thread state), semantic memory (vector search grounded with real citations, not the model's imagination), and episodic memory (structured facts about a specific user that persist across threads), including a custom retrieval tool that returns citation metadata instead of raw text and a remember_fact tool the agent can call to persist what it learns about a user.
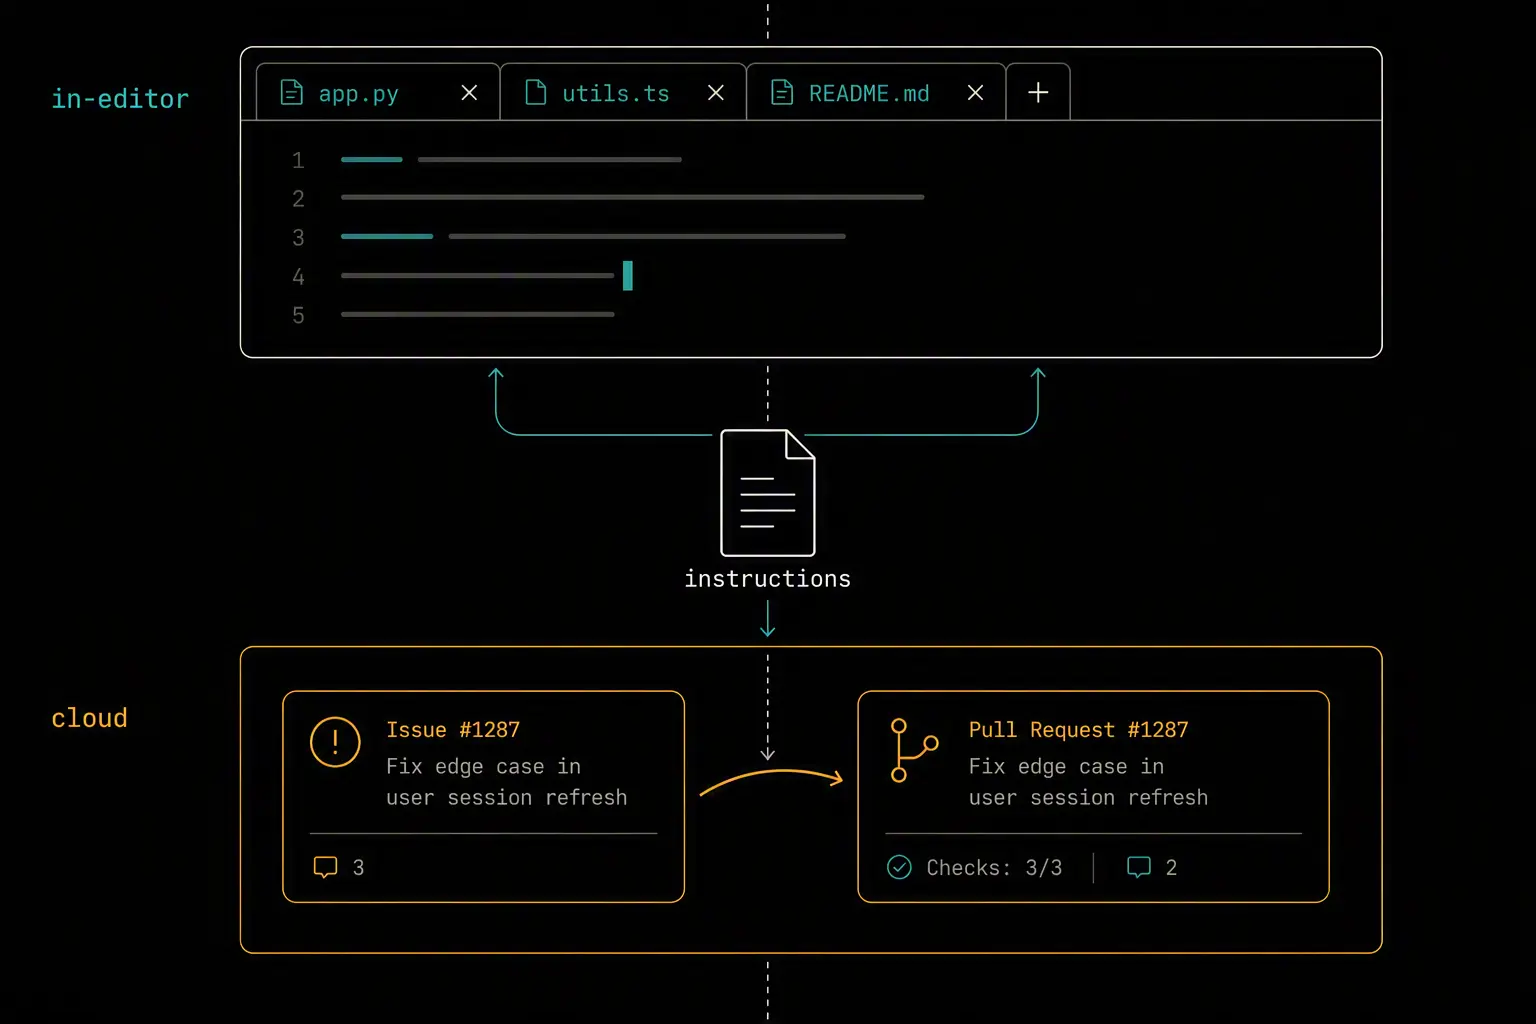
Getting Started with GitHub Copilot: Setup, Environment, and Best Practices
Most teams never get past inline autocomplete. Setting up instructions files, agent mode, and the cloud coding agent turns Copilot into a real project agent.
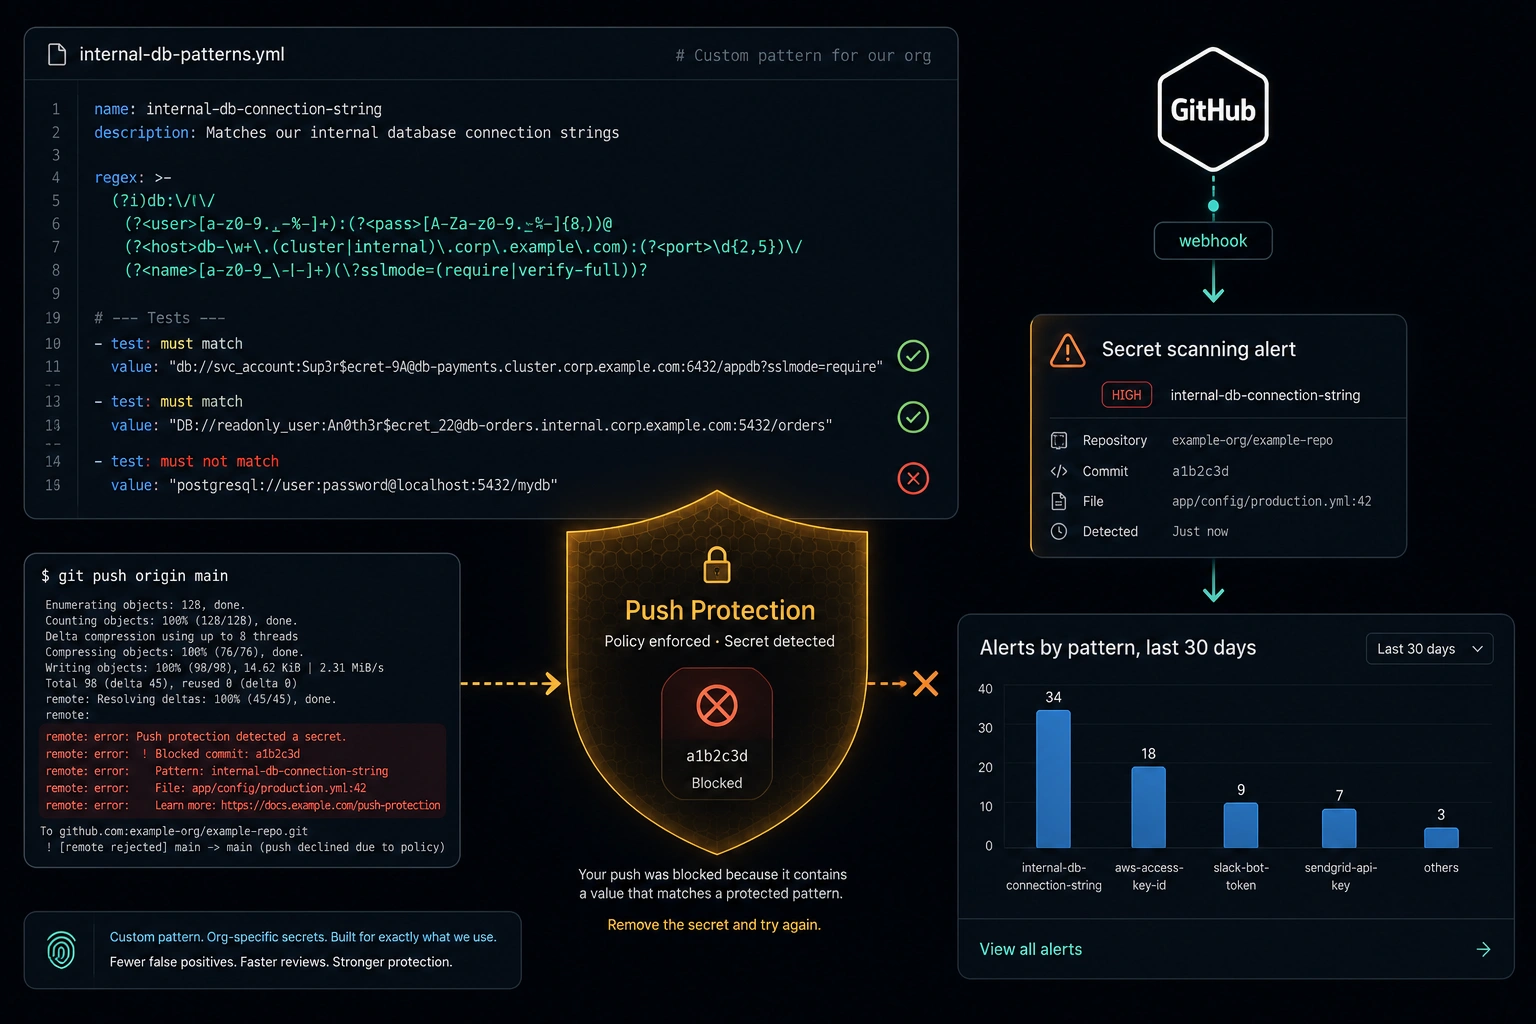
GitHub Secret Scanning Custom Patterns: Finding Business-Specific Credentials Before They Ship
GitHub's built-in secret scanning covers common third-party token formats, but internal API keys, database connection strings, and proprietary credential formats need custom patterns - which most teams never configure. This post covers writing a custom secret scanning pattern with regex and test strings, rolling it out at the org level with a dry run, enabling push protection, and routing alerts to a dashboard, including working patterns for internal API key prefixes, database connection strings, and JWTs from a known issuer.
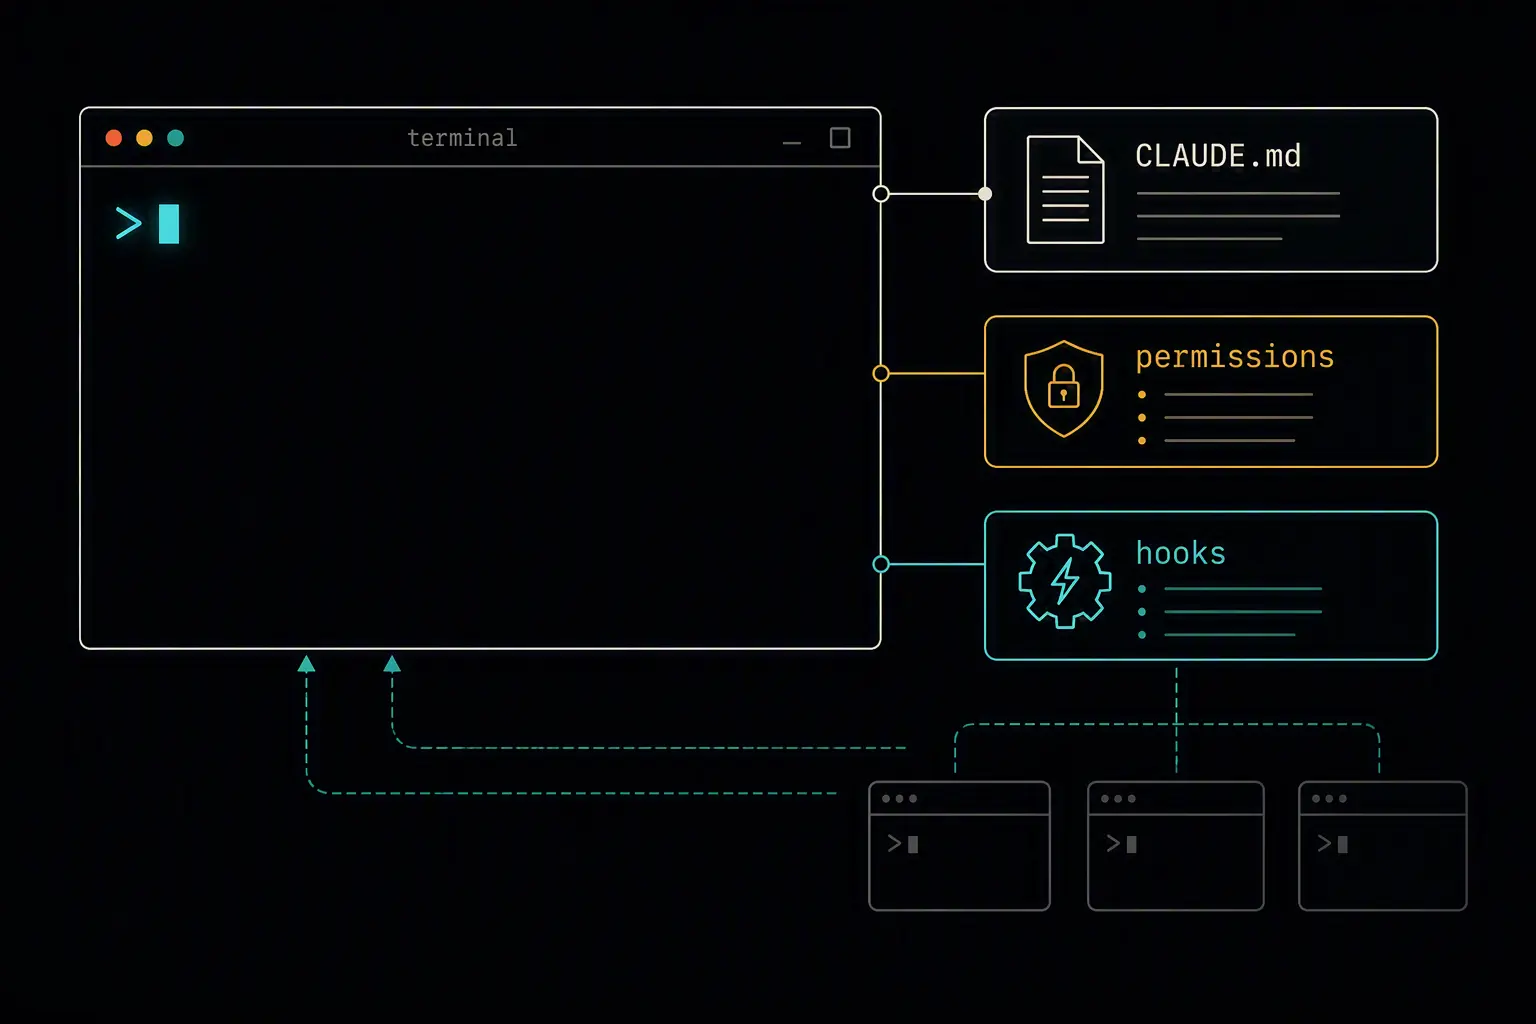
Getting Started with Claude Code: Setup, Environment, and Best Practices
Install takes a minute; the value is in CLAUDE.md, permissions, and hooks. A practical setup guide for making Claude Code a programmable agent, not a chatbot.
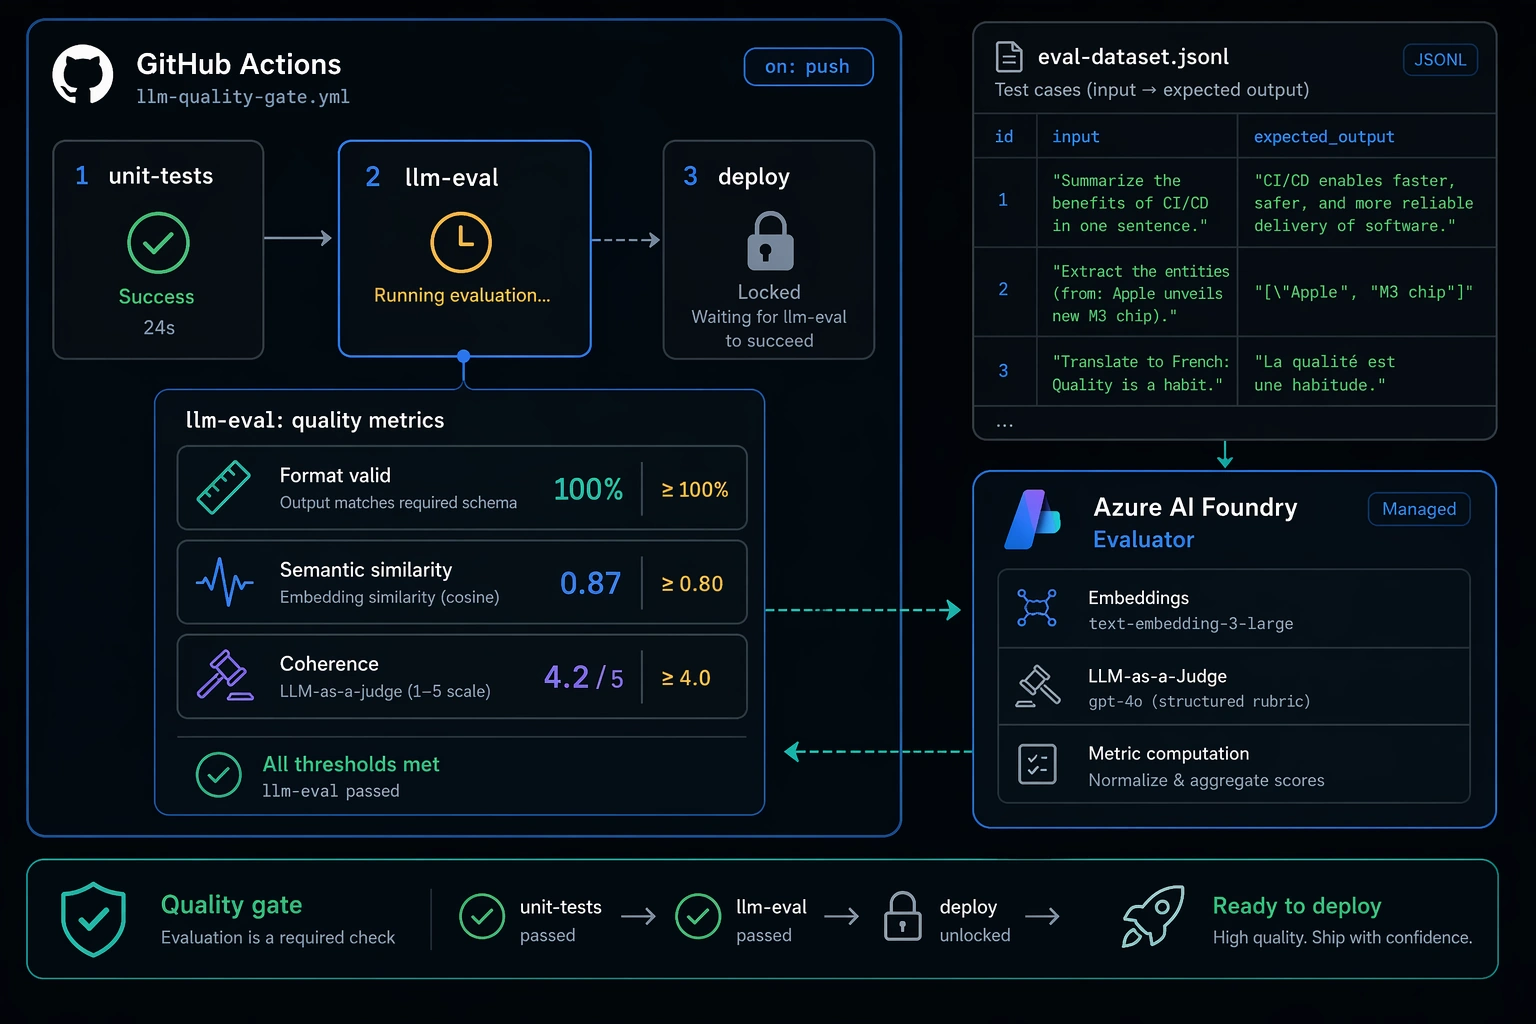
Evaluating LLM Outputs in CI/CD: Testing Your AI Features Like Production Code
AI features that can't be regression-tested are a deployment liability. This post covers how to evaluate LLM outputs in CI as a first-class quality gate: deterministic checks for format and latency, semantic similarity scoring for non-deterministic outputs, LLM-as-judge for subjective quality, and a GitHub Actions workflow that fails the build when evaluation scores drop below threshold using the Azure AI Foundry evaluation SDK.
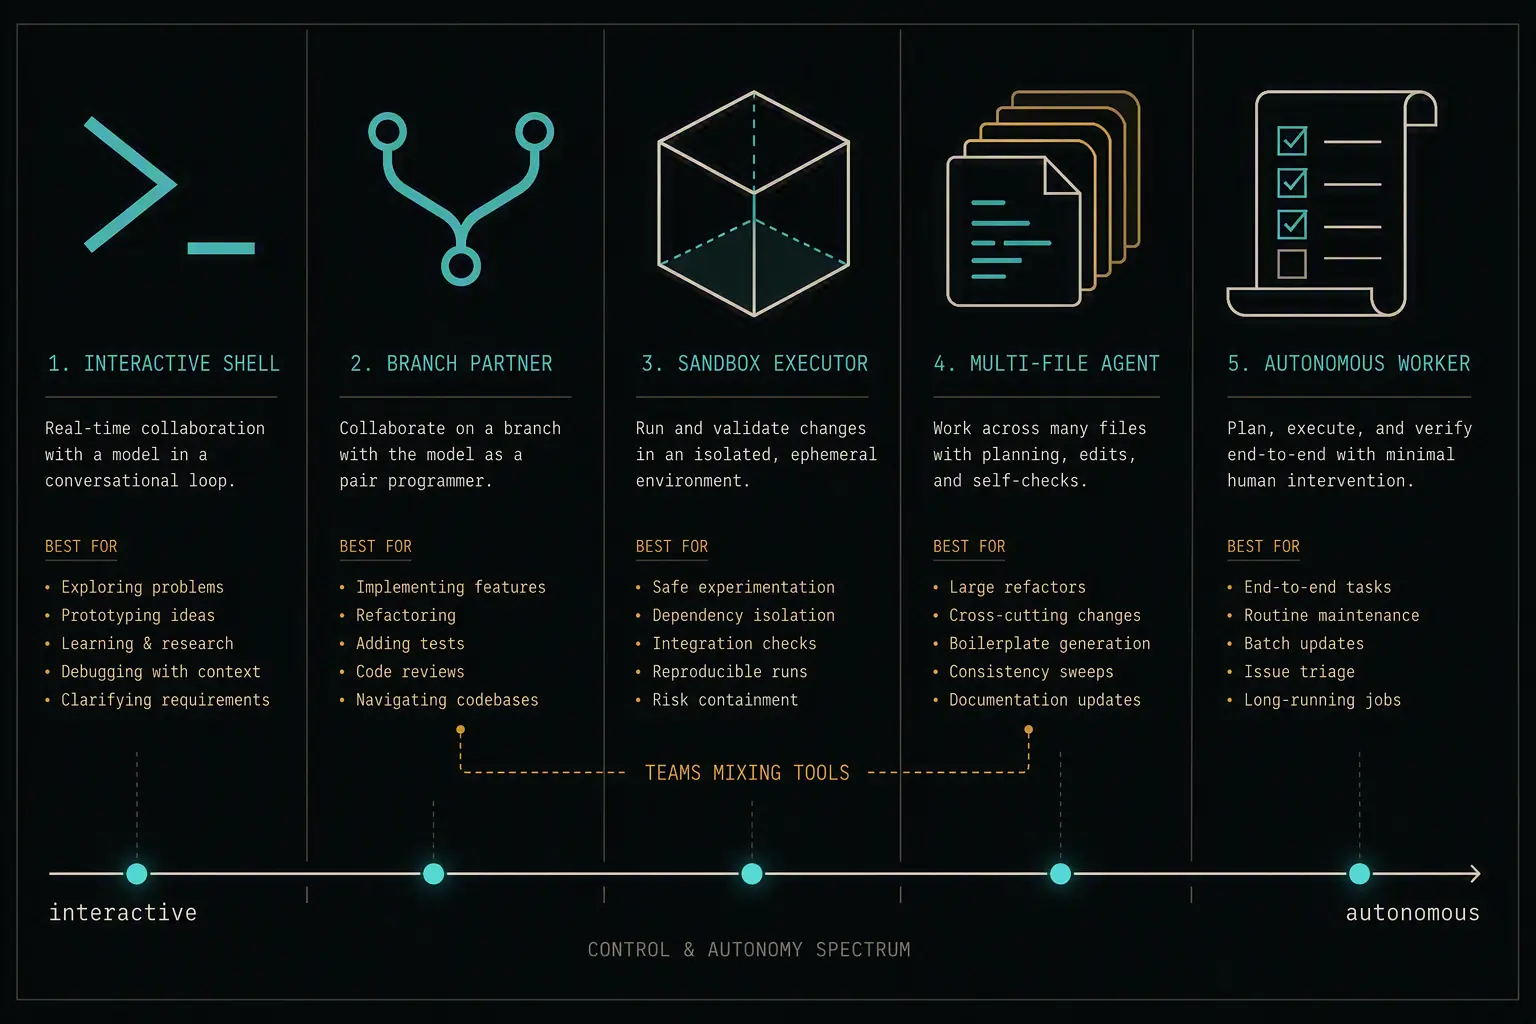
The Top 5 AI Coding Agents Compared: Which One Should You Choose?
Claude Code, Copilot, Codex, Cursor, and Kiro all plan, edit, and ship code - but on very different terms. A practical breakdown of which fits which team.
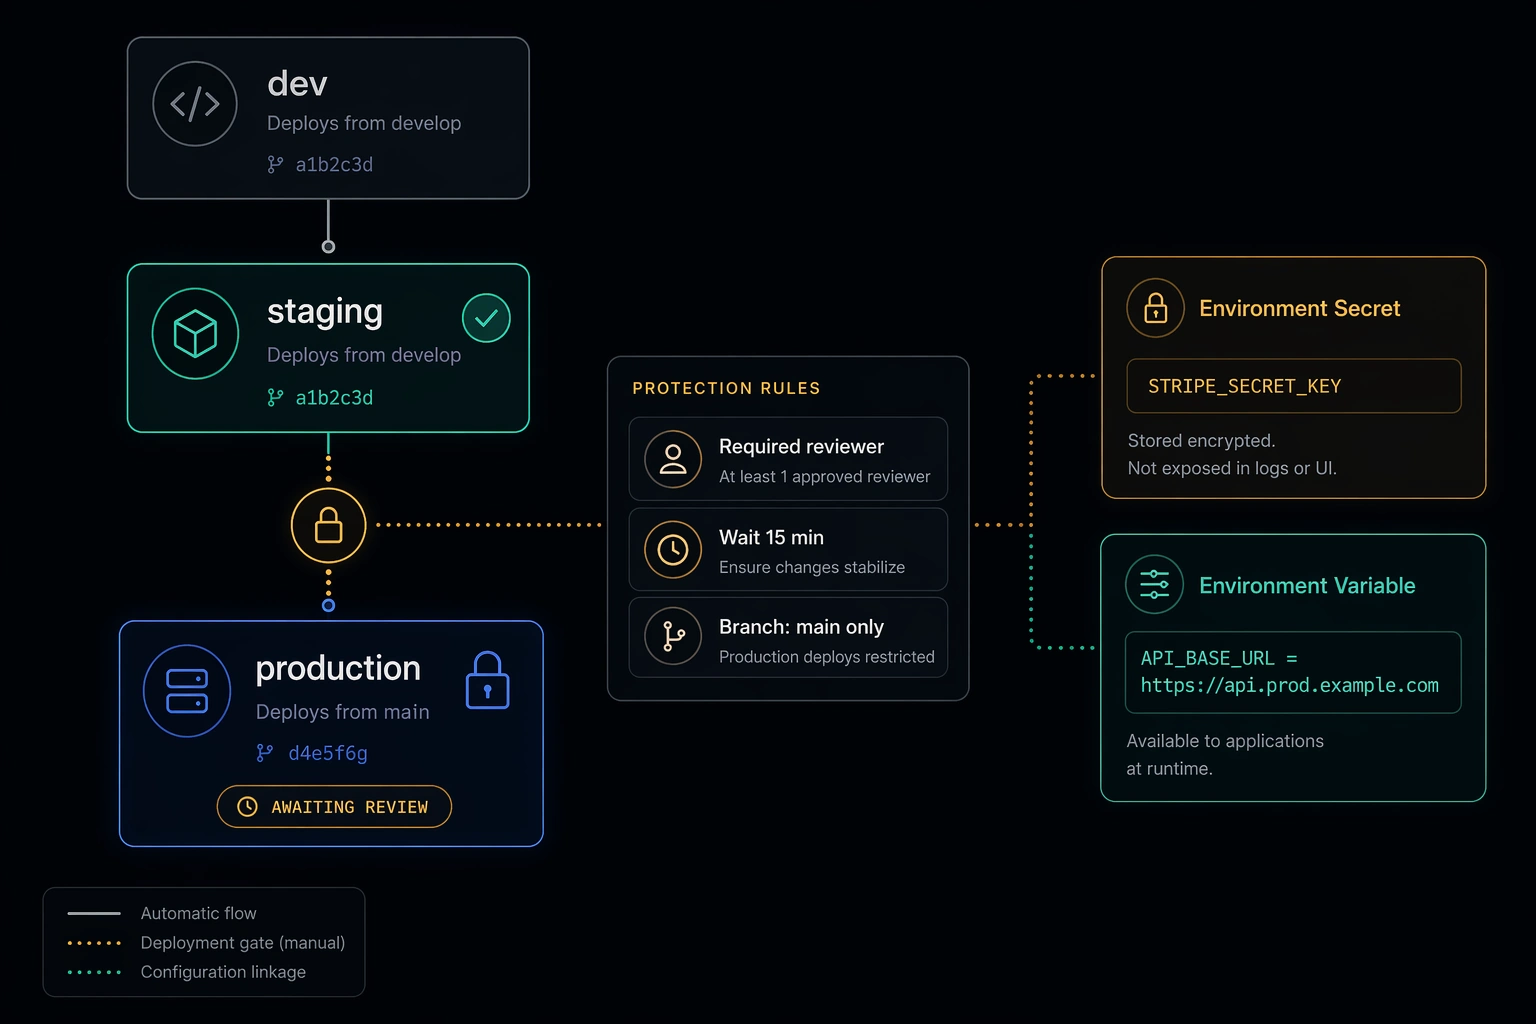
GitHub Environments Deep Dive: Deployment Protection Rules, Secrets, and Variables
GitHub Environments give you a deployment control plane - protection rules, scoped secrets, and per-environment config - but most teams only use required reviewers and stop there. This post covers the full surface: deployment protection rules, the difference between environment and repository secrets, variable promotion across environments, and a workflow that enforces a staging smoke test before production is unlocked.
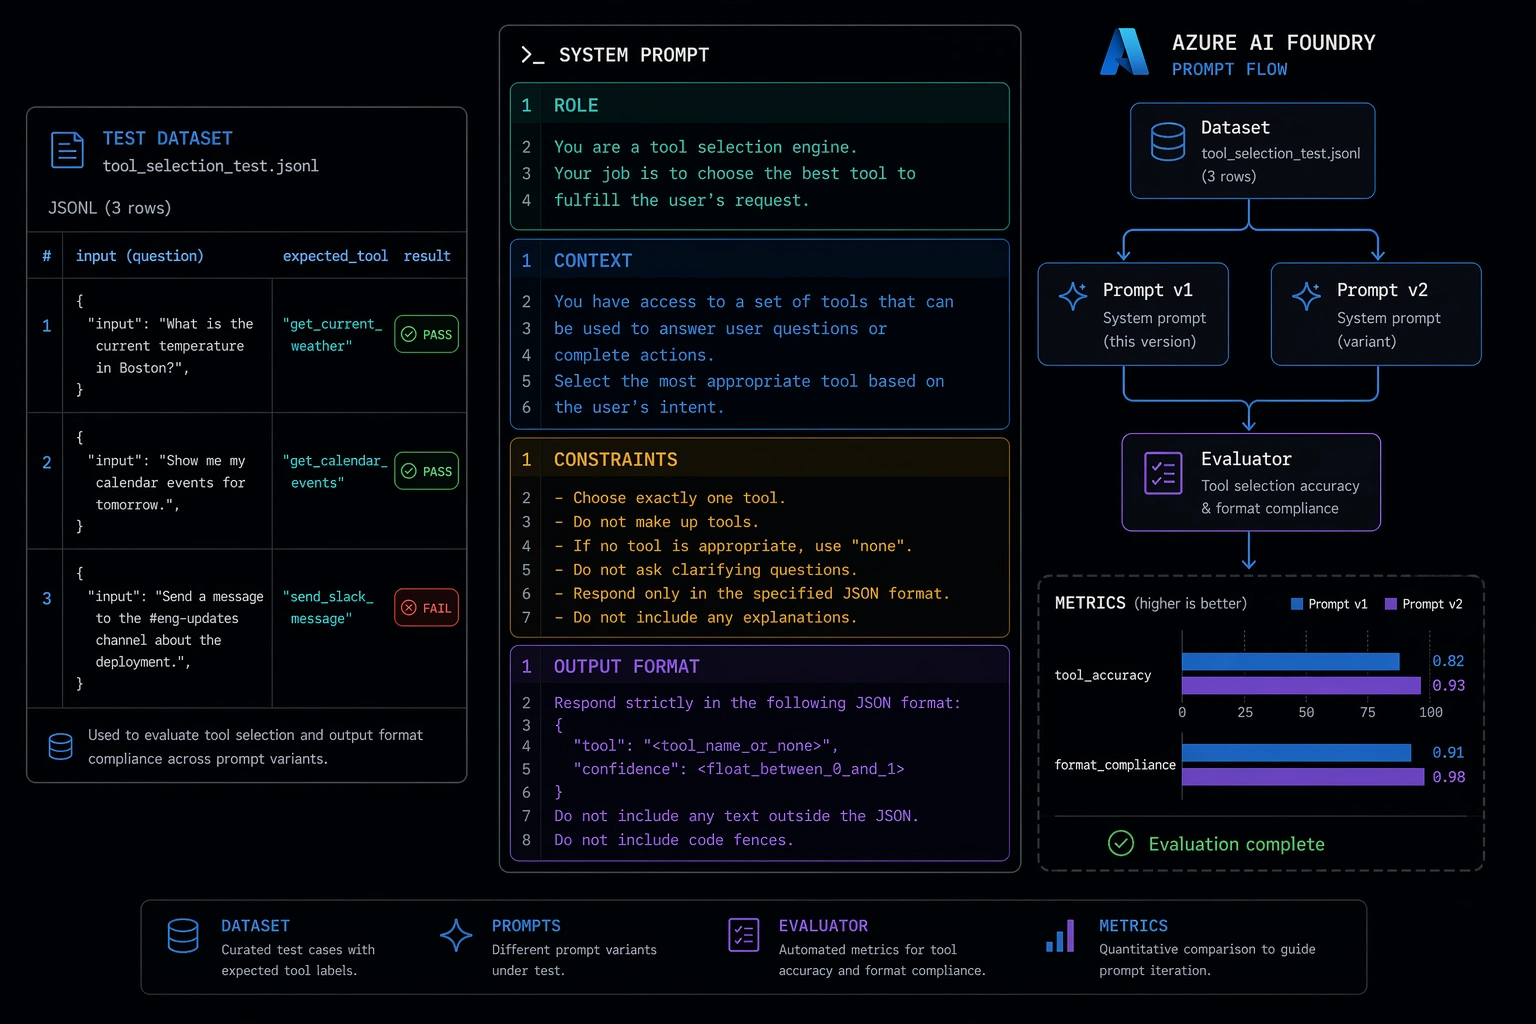
Prompt Engineering for Developers: Writing Reliable Instructions for Agentic Systems
Prompt engineering for agents is not the same discipline as prompting a chatbot. Reliability, tool selection accuracy, and output format consistency matter far more than creativity - and none of those properties survive without systematic testing. This post covers how to structure agent system prompts, calibrate tool selection with few-shot examples, handle ambiguous input gracefully, and test prompt changes using Azure AI Foundry's prompt flow.
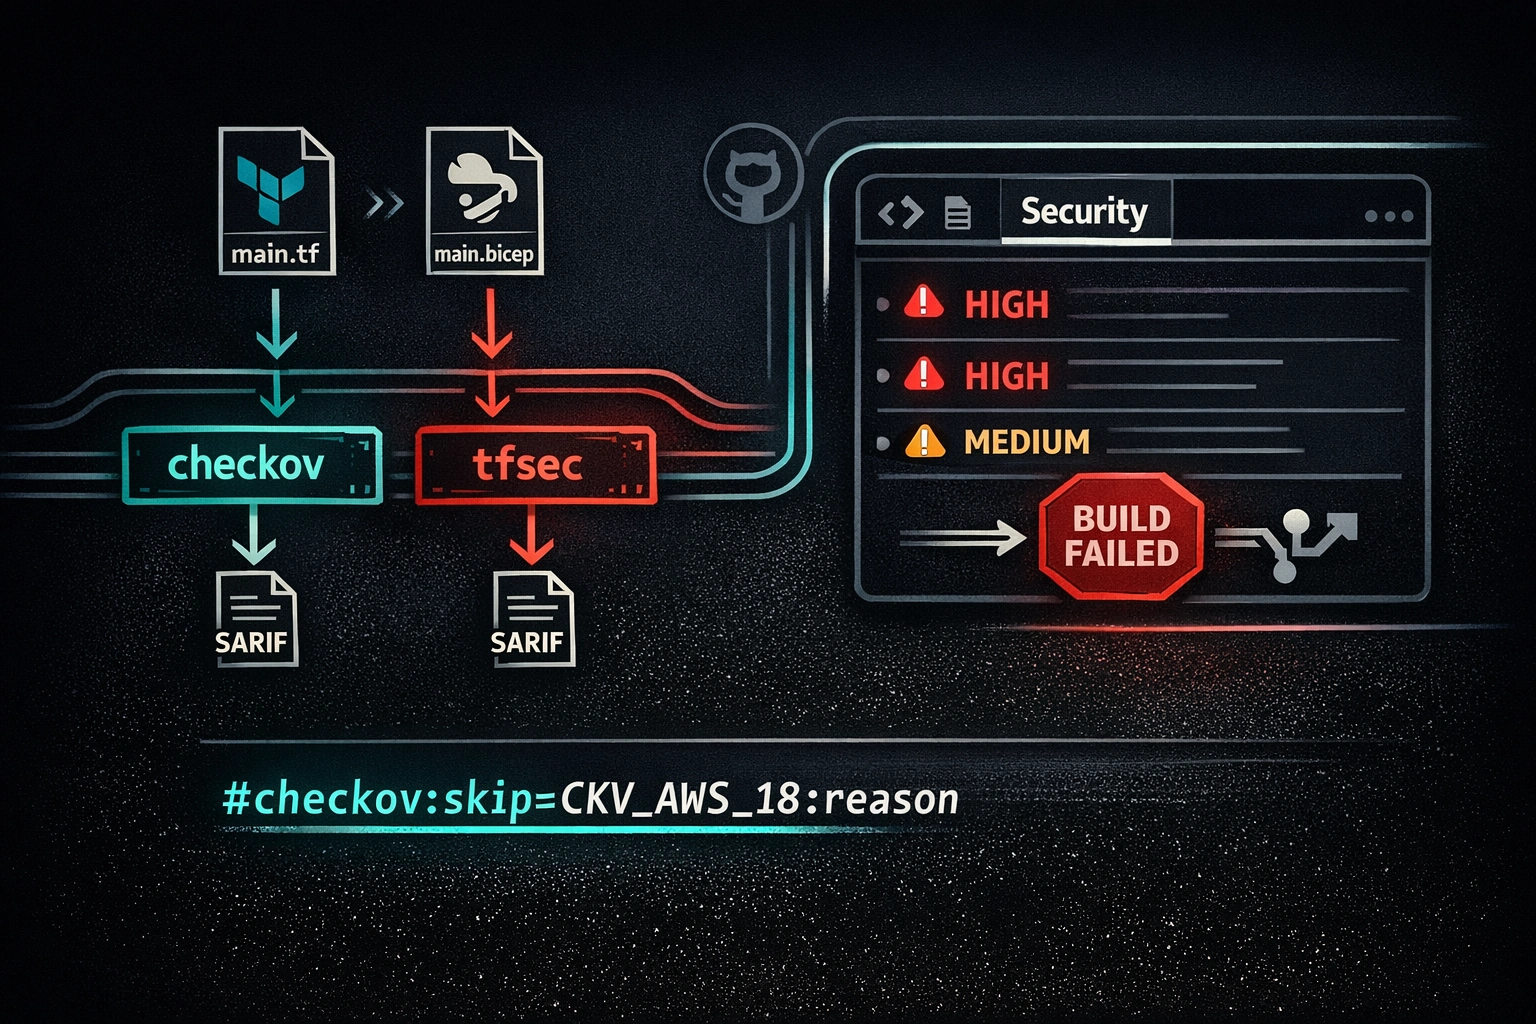
IaC Security Scanning in CI: Catching Terraform and Bicep Misconfigurations Before They Deploy
Misconfigured infrastructure is one of the most common causes of cloud security incidents. Catching it in CI costs nothing compared to fixing it post-deployment. Here's how to integrate Checkov and tfsec for Terraform, and PSRule for Bicep, into a GitHub Actions workflow that blocks on high-severity findings and surfaces everything else in the GitHub Security tab.
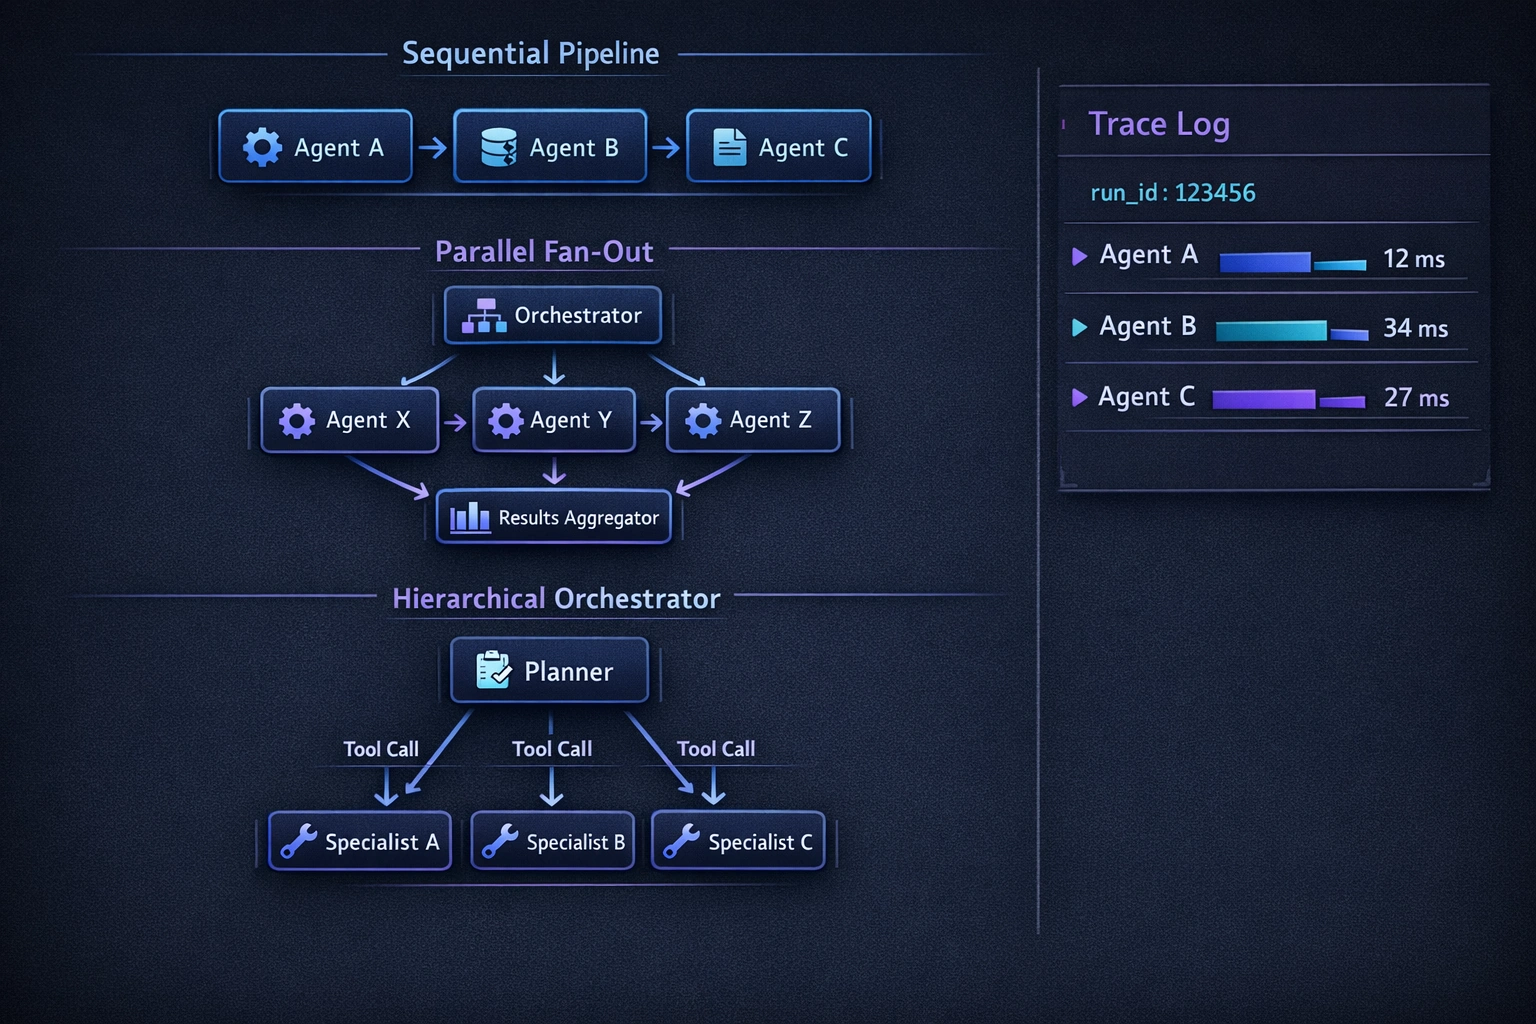
Multi-Agent Patterns with Azure AI Foundry: Orchestration, Handoff, and Shared State
Single agents hit a ceiling fast - context window limits, generalization tradeoffs, and latency add up. The fix isn't a bigger model; it's the right orchestration pattern. This post covers the three core multi-agent patterns with concrete Azure AI Foundry implementations: sequential pipeline, parallel fan-out, and hierarchical orchestrator/sub-agent, plus shared state, error handling, and observability.
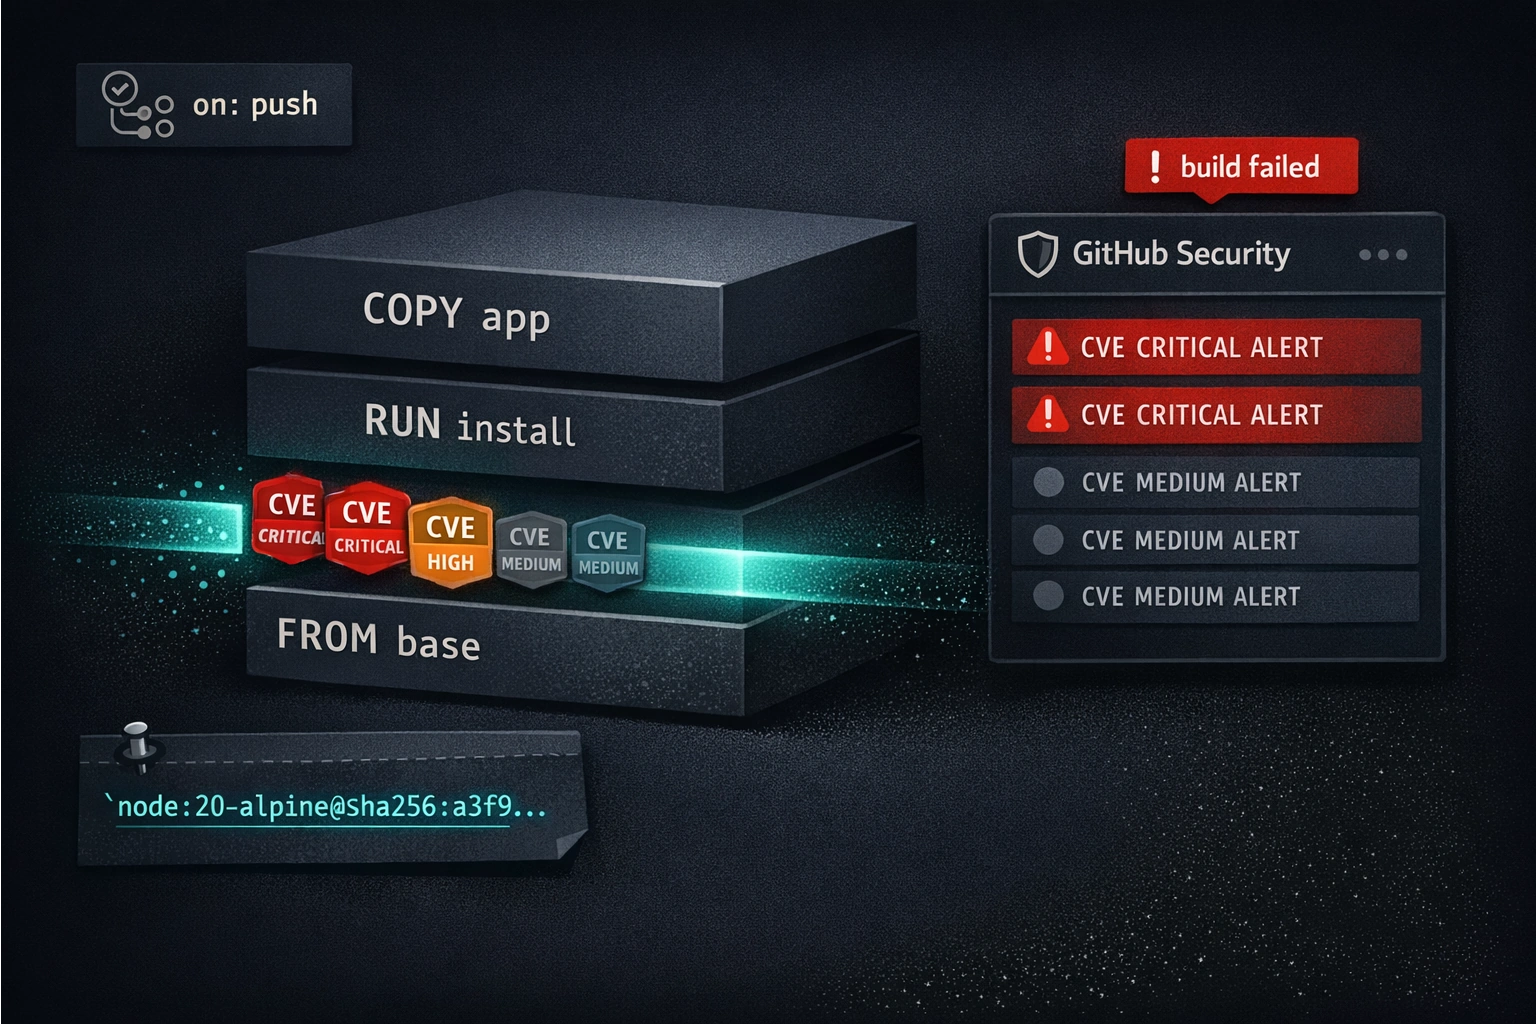
Container Image Security in CI: Scanning with Trivy and GitHub Advanced Security
Most teams run Trivy and get back 200 alerts they don't act on. The scanner isn't the problem - the workflow design is. Here's how to configure Trivy in GitHub Actions to produce signal: SARIF upload to the GitHub Security tab, severity thresholds that block on what you can fix, and a policy for unfixable CVEs in base images.
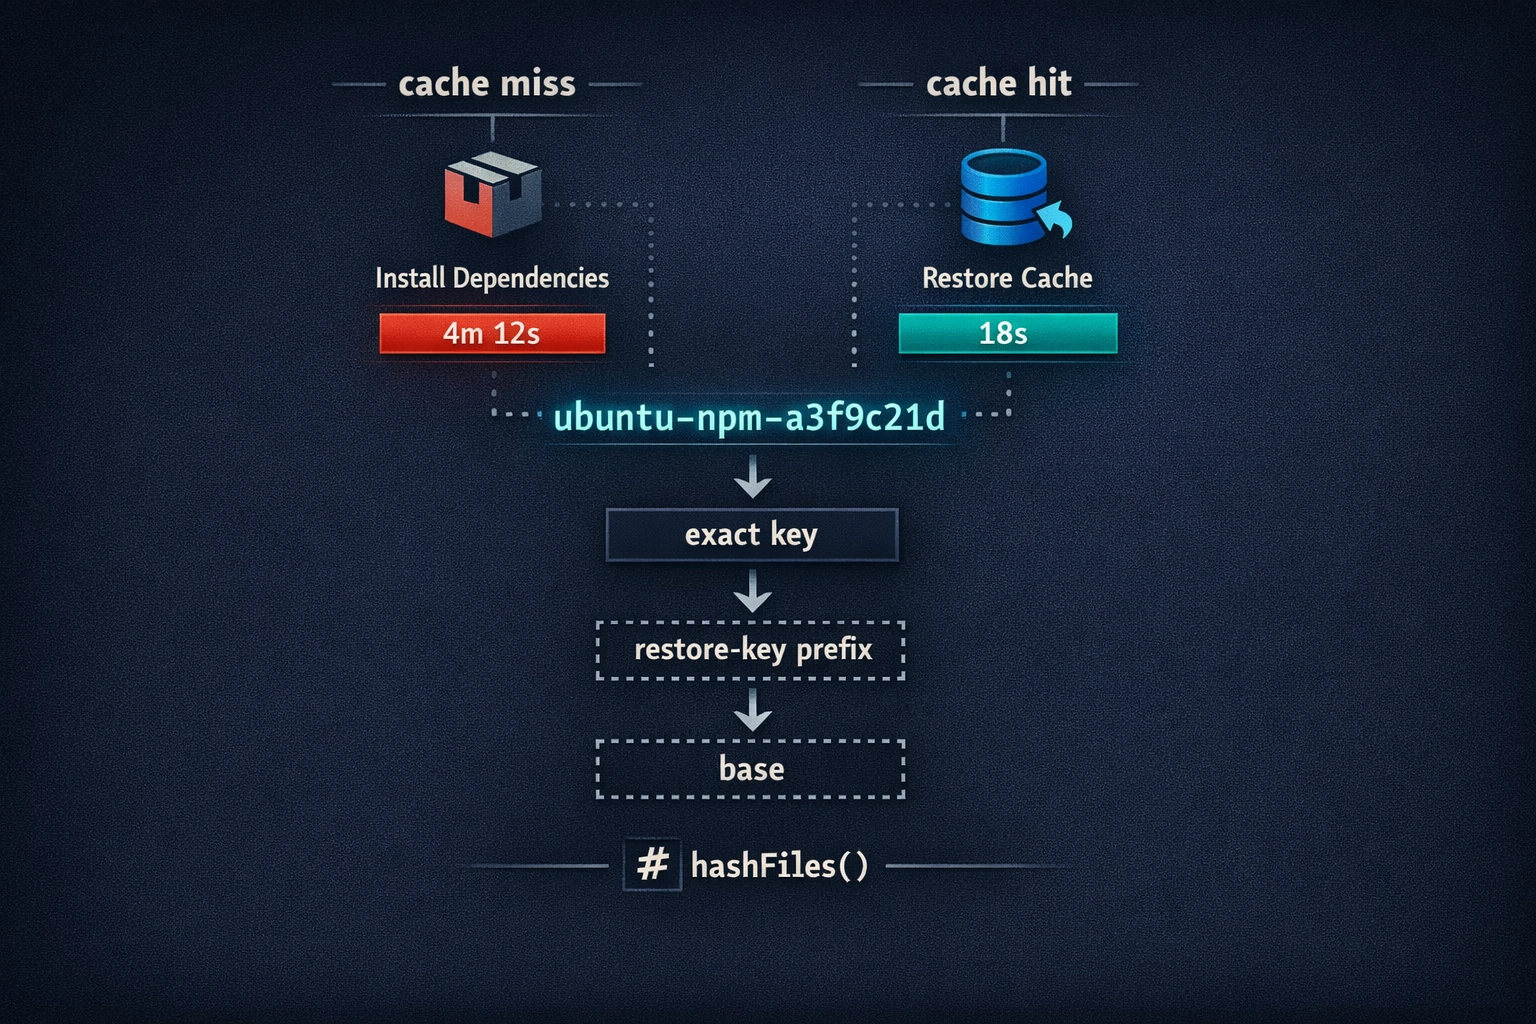
GitHub Actions Advanced Caching: Strategies That Actually Cut Build Times
Most teams use actions/cache with a single key and accept 20% hit rates as inevitable. They're not. Cache key strategy - how you compose the key, chain restore-keys fallbacks, scope by branch, and handle matrix builds - is the difference between a dependency install that takes 4 minutes and one that takes 18 seconds.
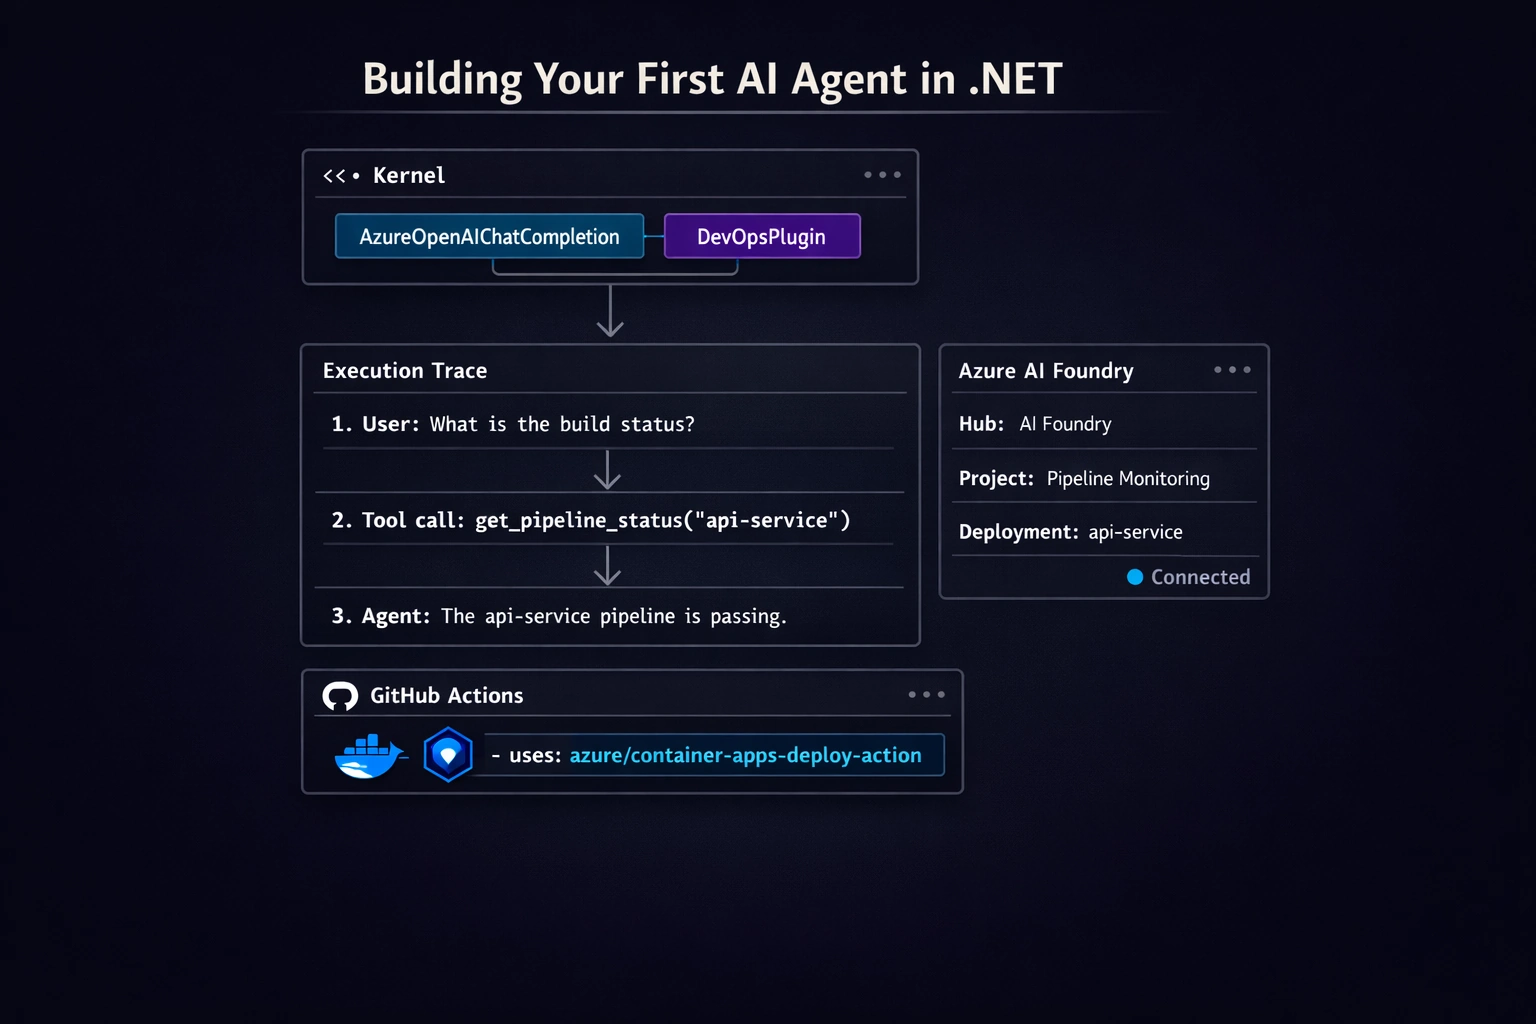
Semantic Kernel and Azure AI Foundry: Building Your First AI Agent in .NET
Semantic Kernel is Microsoft's open-source SDK for building AI agents. Azure AI Foundry is where you deploy the model. Together they give .NET developers a production-ready agent path - the same orchestration-plus-hosting story Python teams get from LangChain, without leaving the Microsoft ecosystem. This post builds a working agent end-to-end.
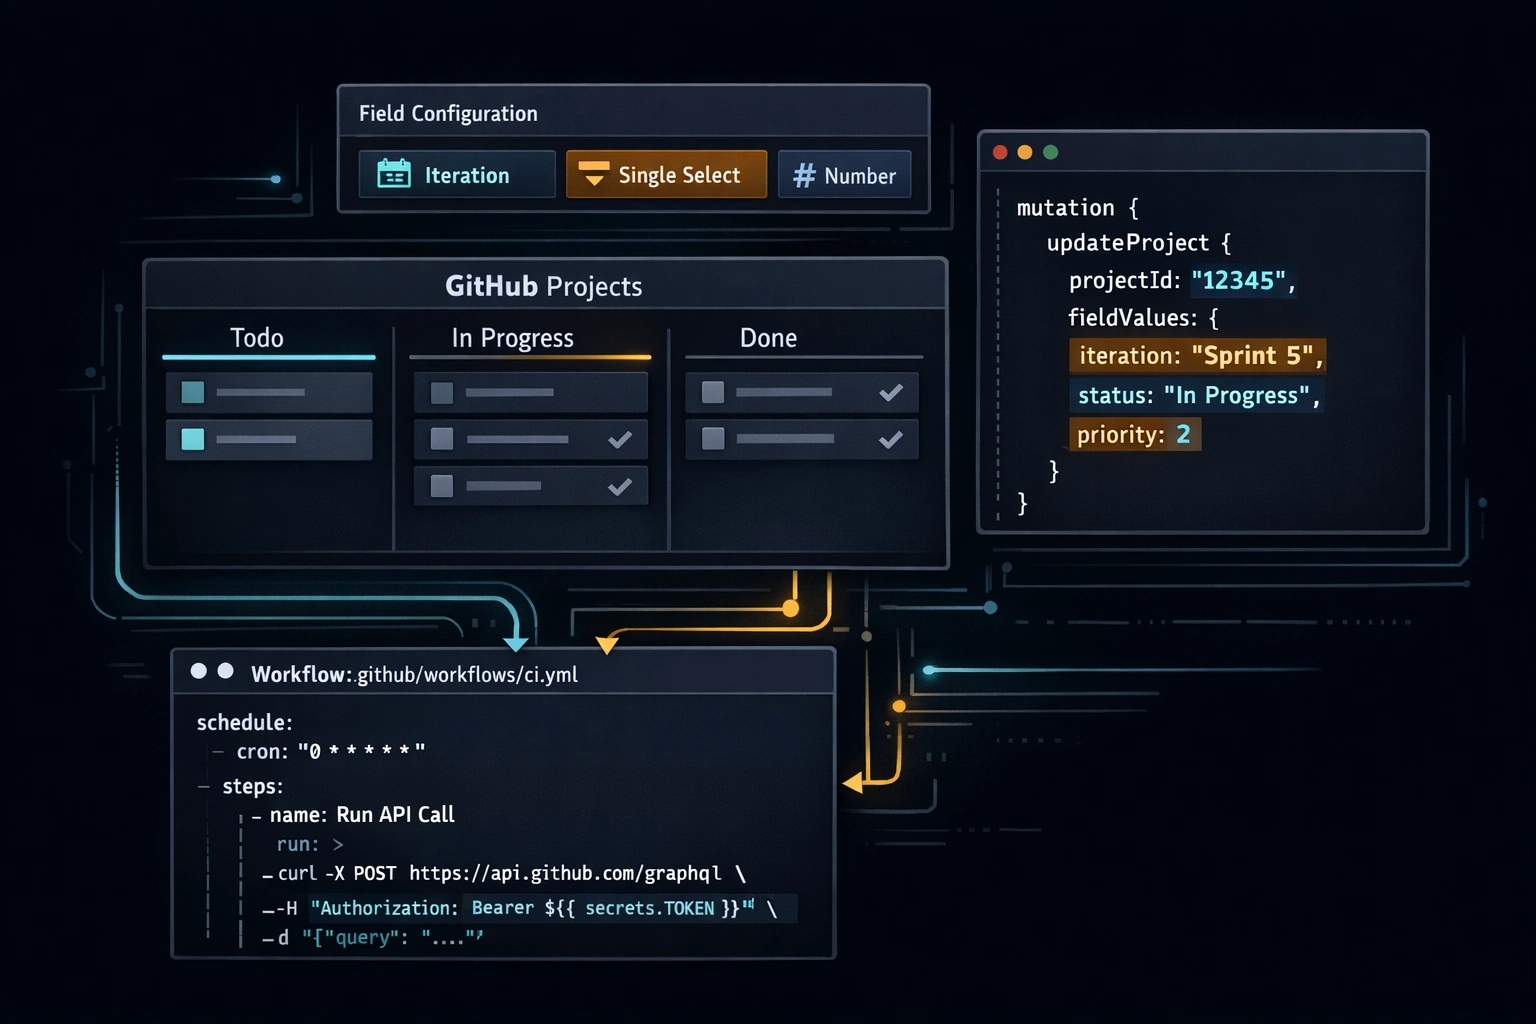
GitHub Projects Automation: Custom Fields, Workflows, and the GraphQL API
GitHub Projects v2 ships with a GraphQL API, custom field types, and built-in workflow triggers that most teams never configure. This post shows how to wire them together: auto-assign sprints, sync PR status to issue state, and generate a weekly digest - all without leaving GitHub.
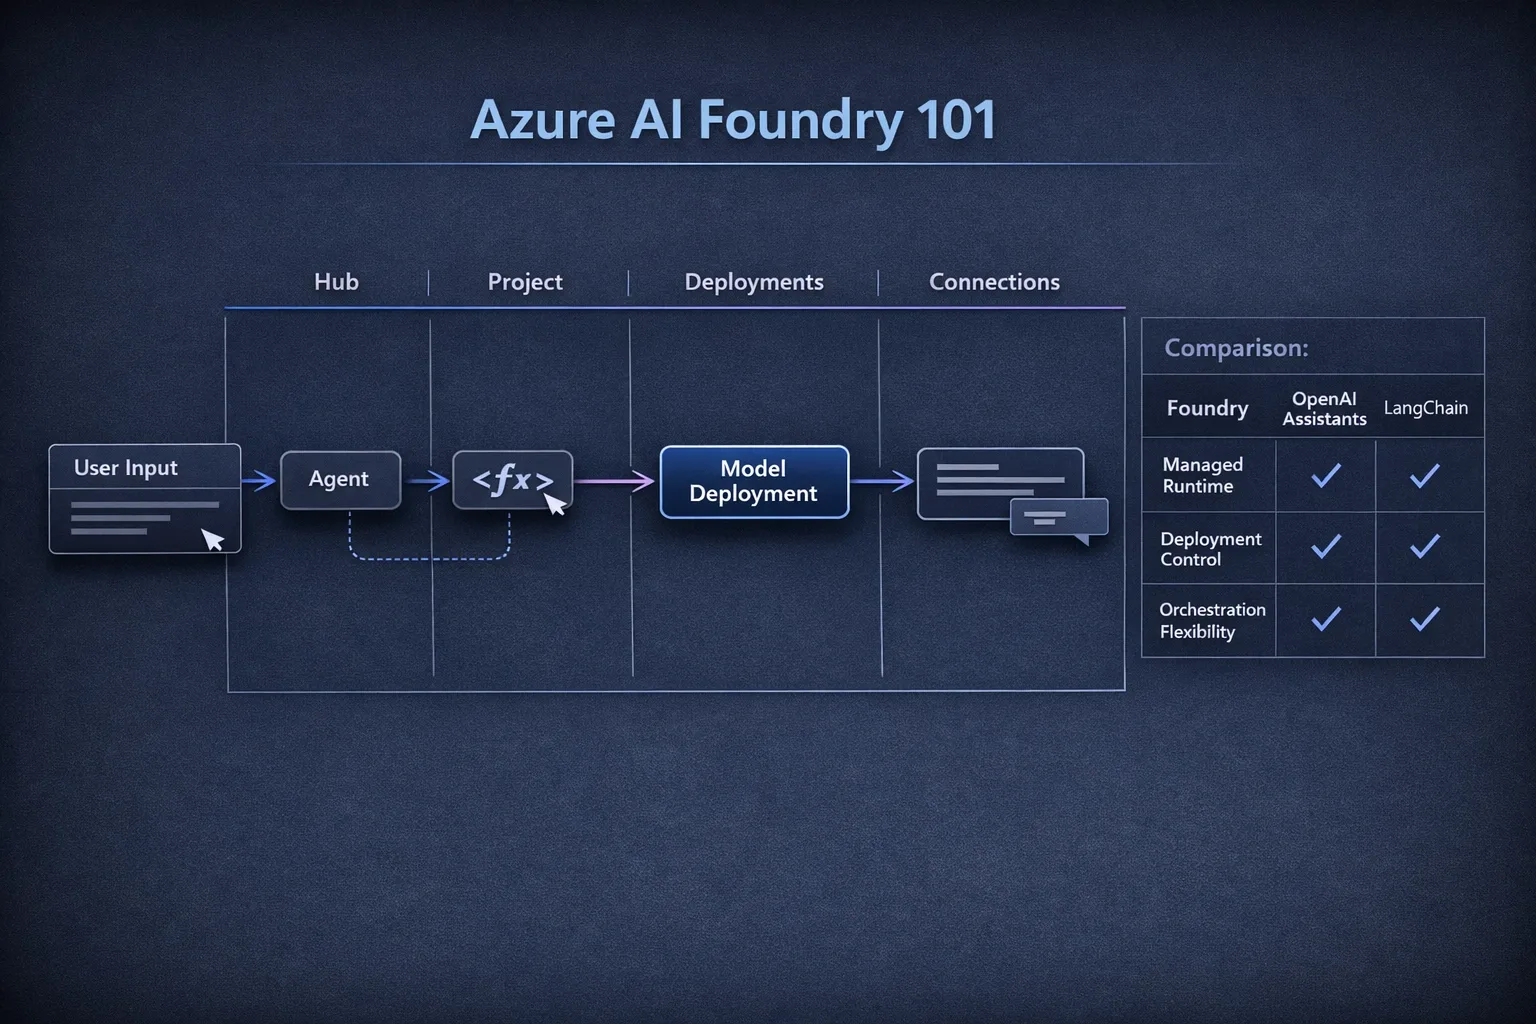
Azure AI Foundry: A Developer's First Look at Agentic AI Workflows
Azure AI Foundry is easiest to understand when you treat it as app infrastructure for agents: define a project, deploy a model, wire connections, add a tool, and run. This guide walks through that exact first workflow and maps it to OpenAI Assistants and LangChain concepts.
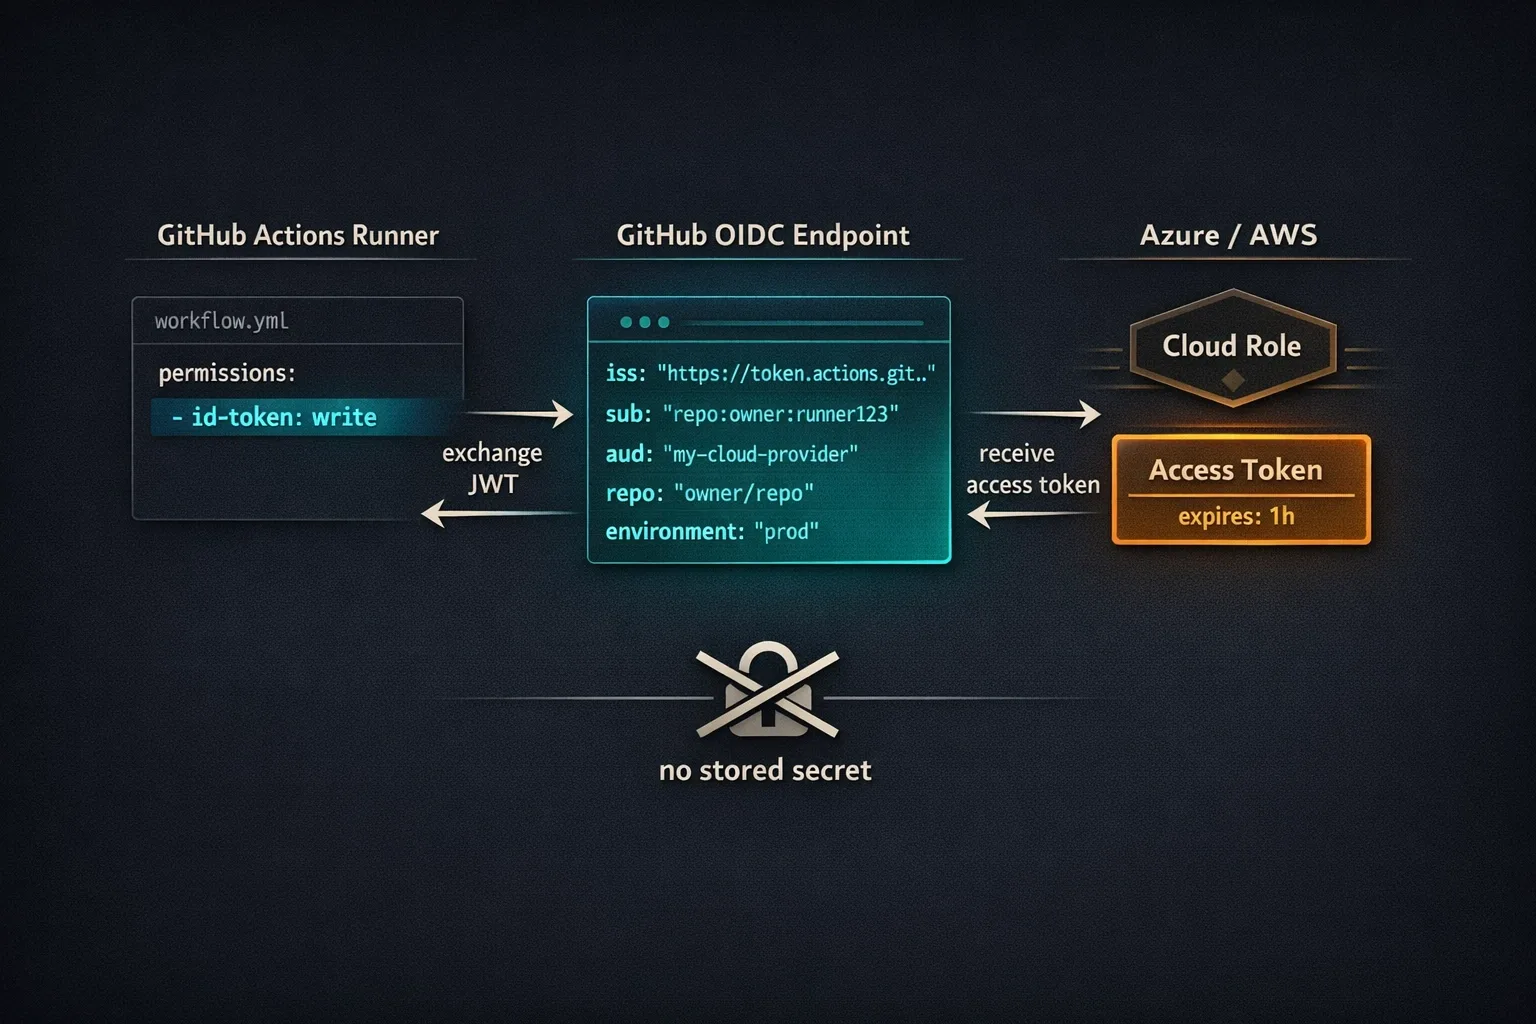
OpenID Connect in GitHub Actions: Replacing Long-Lived Secrets with Short-Lived Tokens
Storing cloud credentials as GitHub secrets is unnecessary and risky - OIDC lets your workflows authenticate to Azure and AWS by exchanging a short-lived GitHub token for a short-lived cloud token, with no static secret anywhere in the chain.
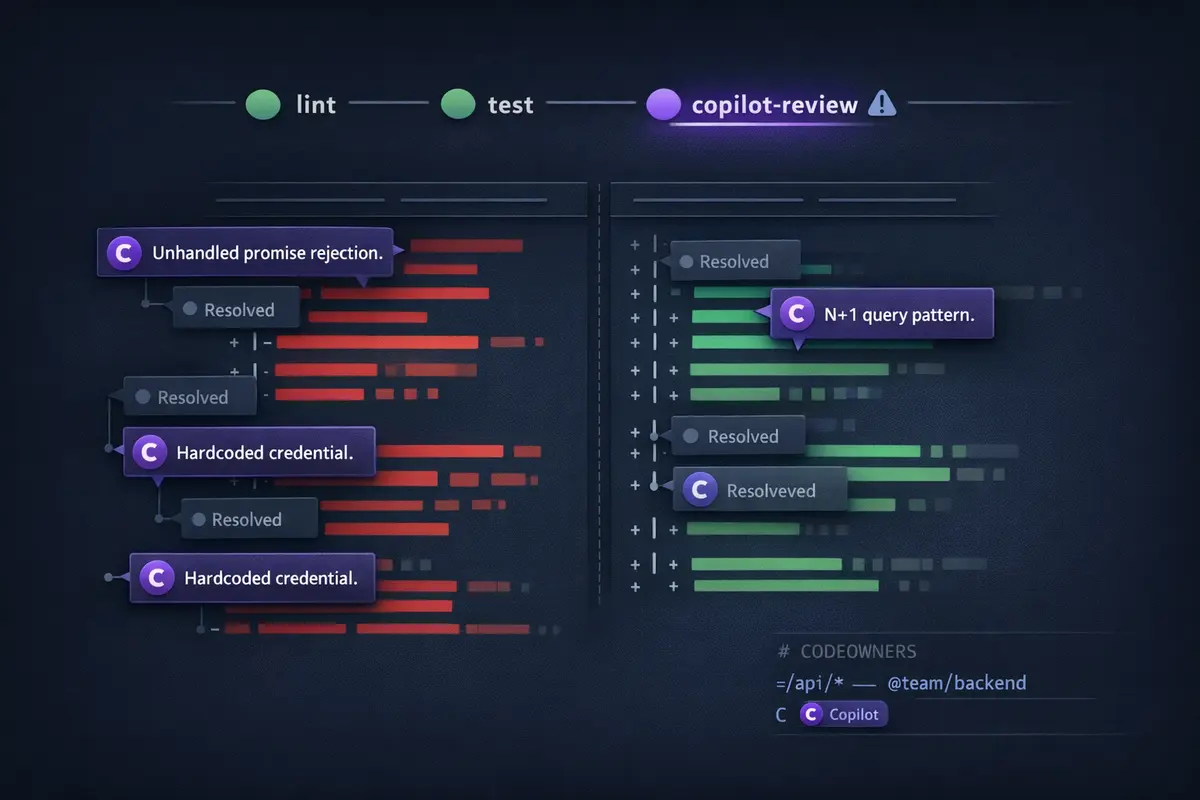
GitHub Copilot in CI: Automating Code Review at Scale
GitHub Copilot code review runs on every PR automatically and flags real issues - but only if you configure it correctly, constrain what it reviews, and treat its output as advisory signal rather than a hard gate.
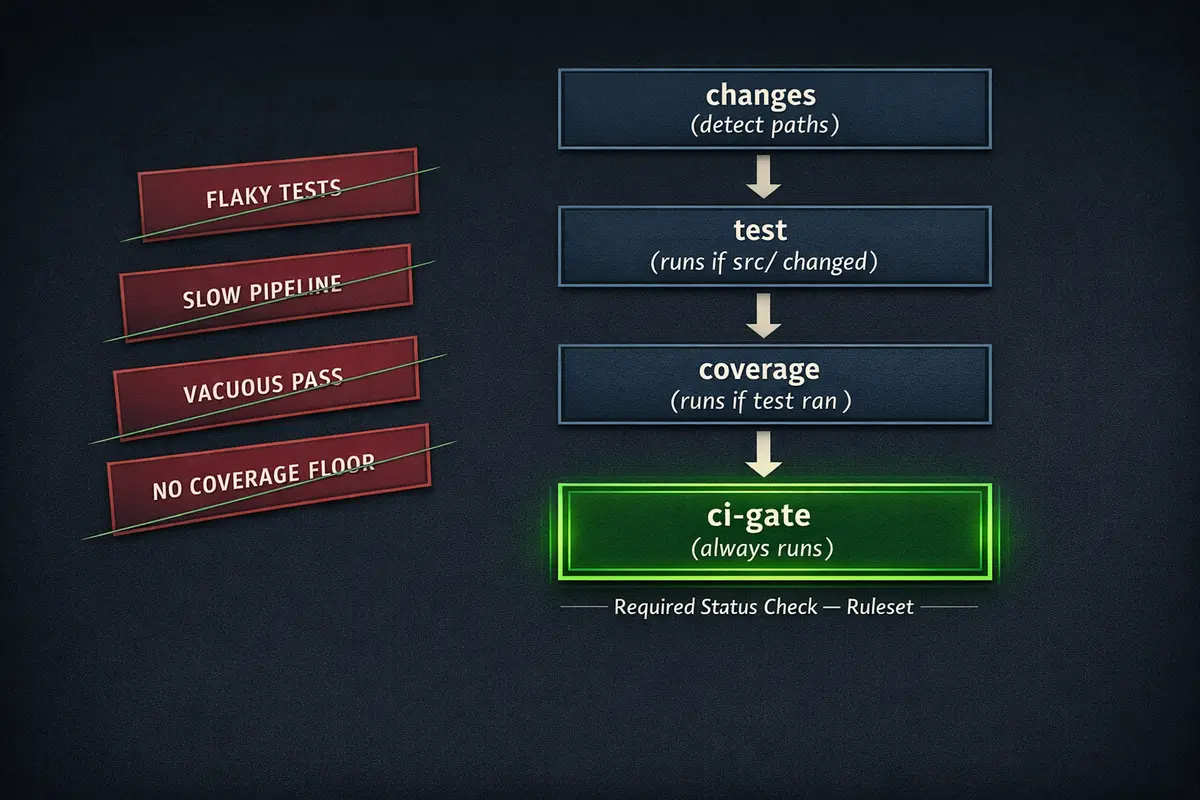
Enforcing Code Quality with GitHub Actions Status Checks You Can Actually Trust
Status checks only block bad code if they are fast, reliable, correctly named, and actually enforced - this post covers the four ways pipelines fail that test and the concrete workflow patterns that fix each one.
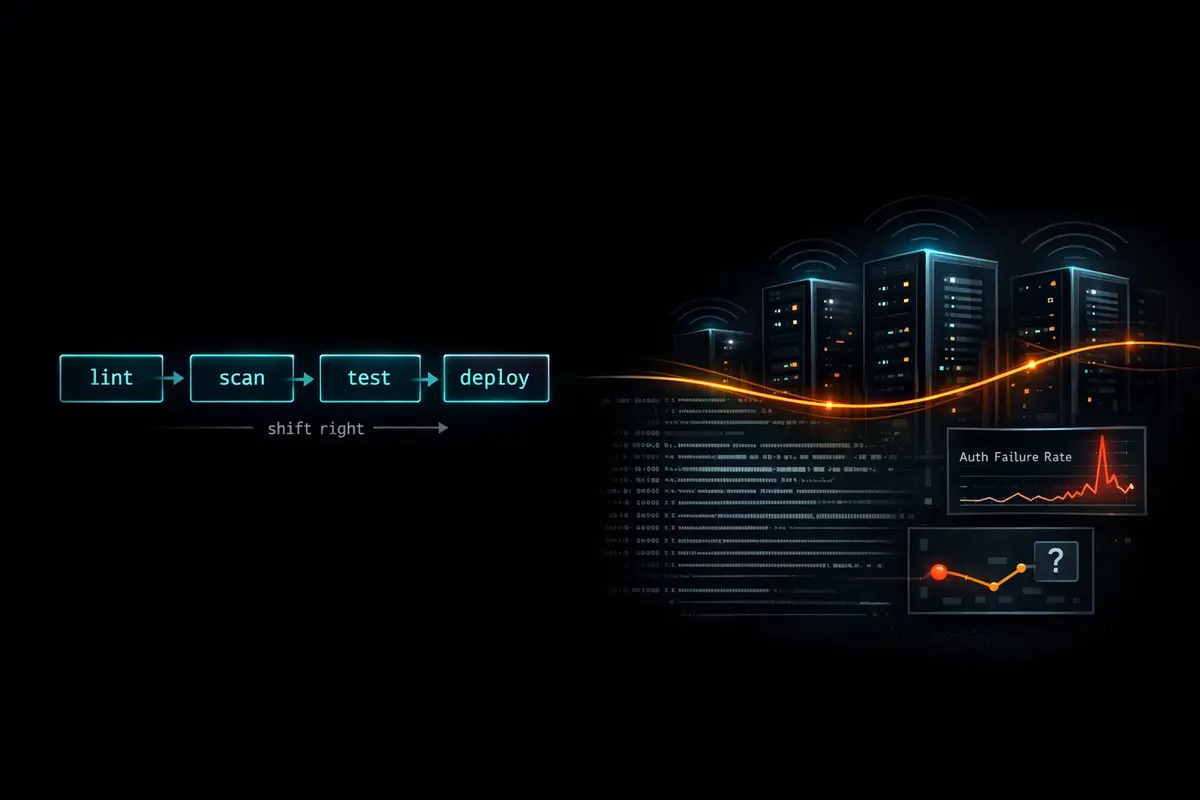
Shift Right: Why Production Observability Is a Security Practice
Shift-left tooling stops at the deployment boundary - runtime observability closes the gap by turning the same logs and traces you already collect into a security detection layer.
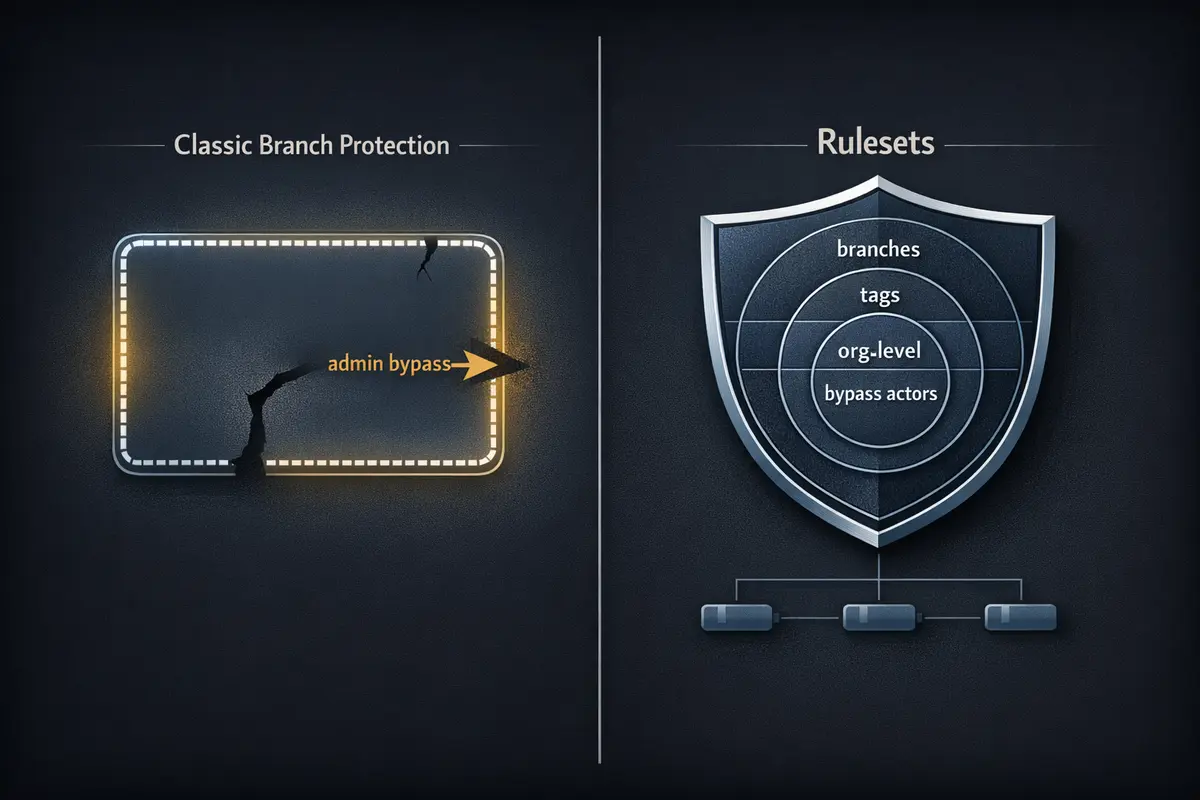
GitHub Branch Protection Rules vs. Rulesets: The New Way to Enforce Standards
GitHub Rulesets replace classic branch protection with organization-level enforcement, named bypass actors, and tag protection - here is what changed, what to migrate first, and an audit workflow to check coverage across your entire org.
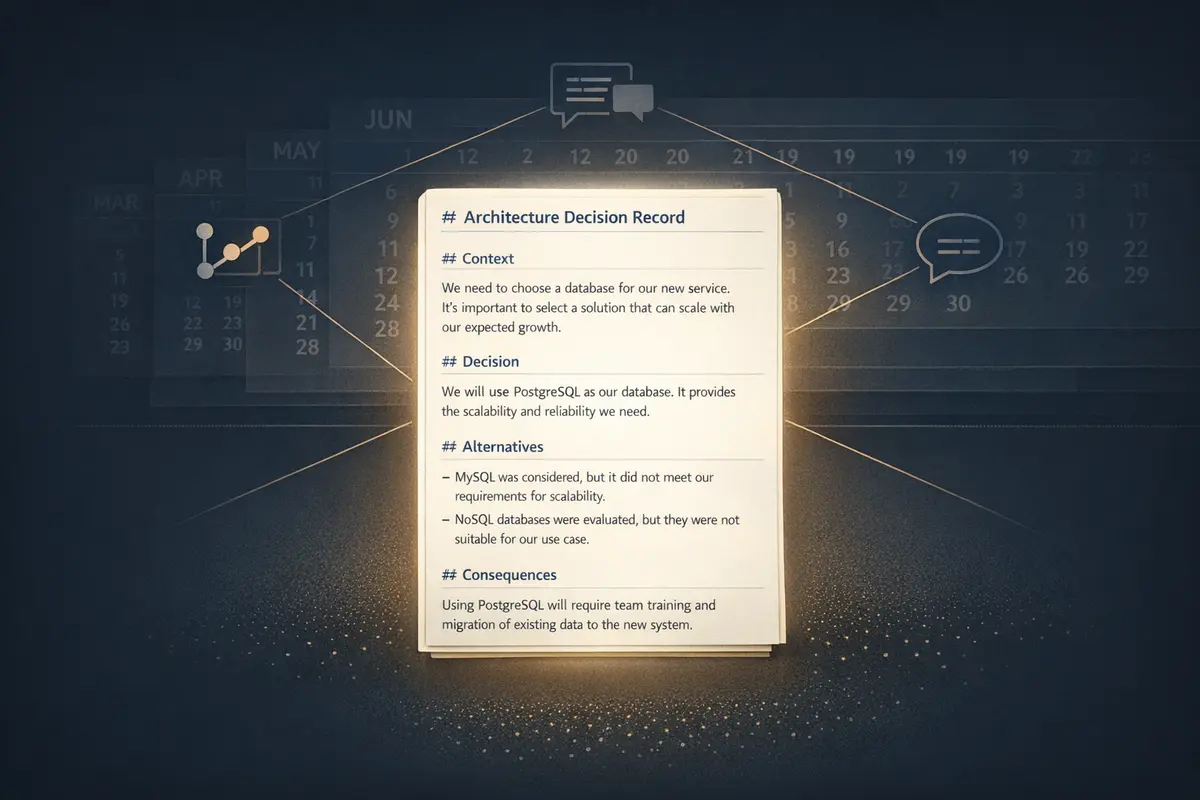
Architecture Decision Records: The 30-Minute Investment That Pays Off for Years
Architecture Decision Records are a single Markdown file per decision that eliminates the 'why did we build it this way?' archaeology session forever - here is the template, the storage convention, the GitHub workflow, and a real example from this blog's own stack.
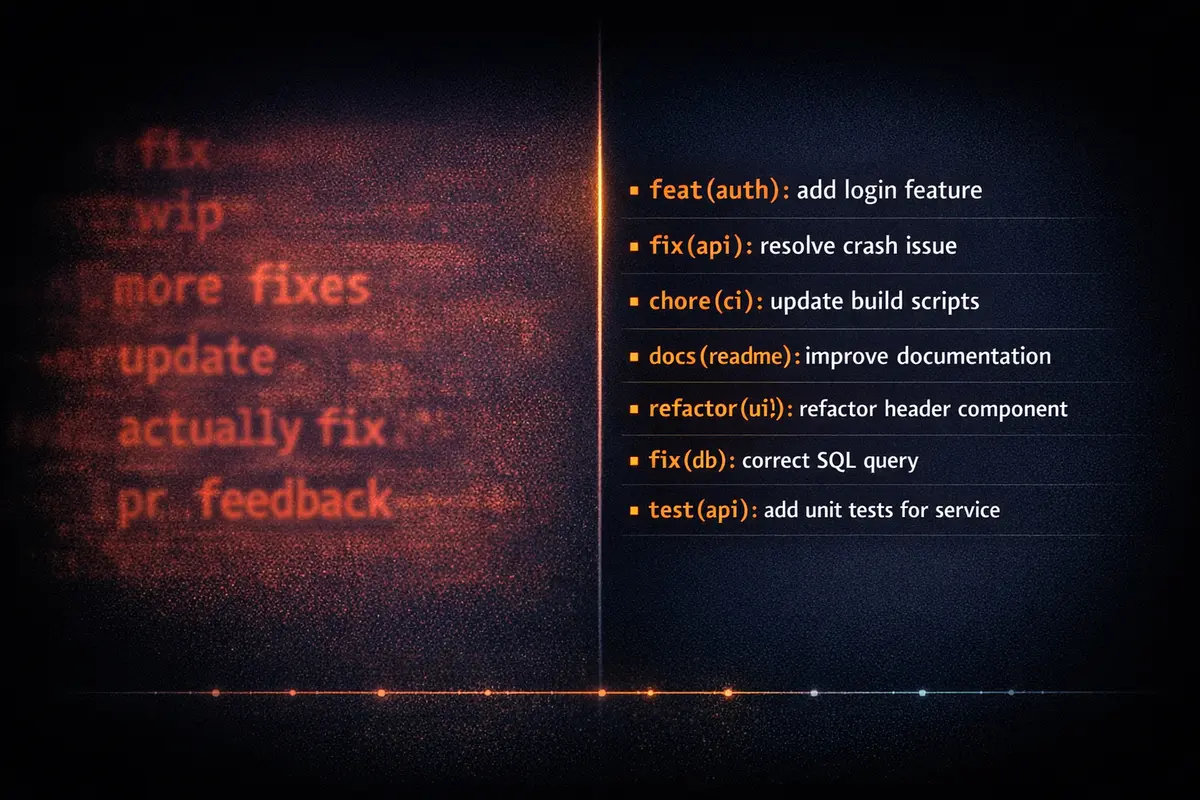
Writing Commit Messages That Make Code Review Faster
Most commit messages are a form of passive negligence - this post teaches the exact format, body-writing discipline, hook setup, and CI enforcement that turns git log into a searchable record of every decision your team has ever made.
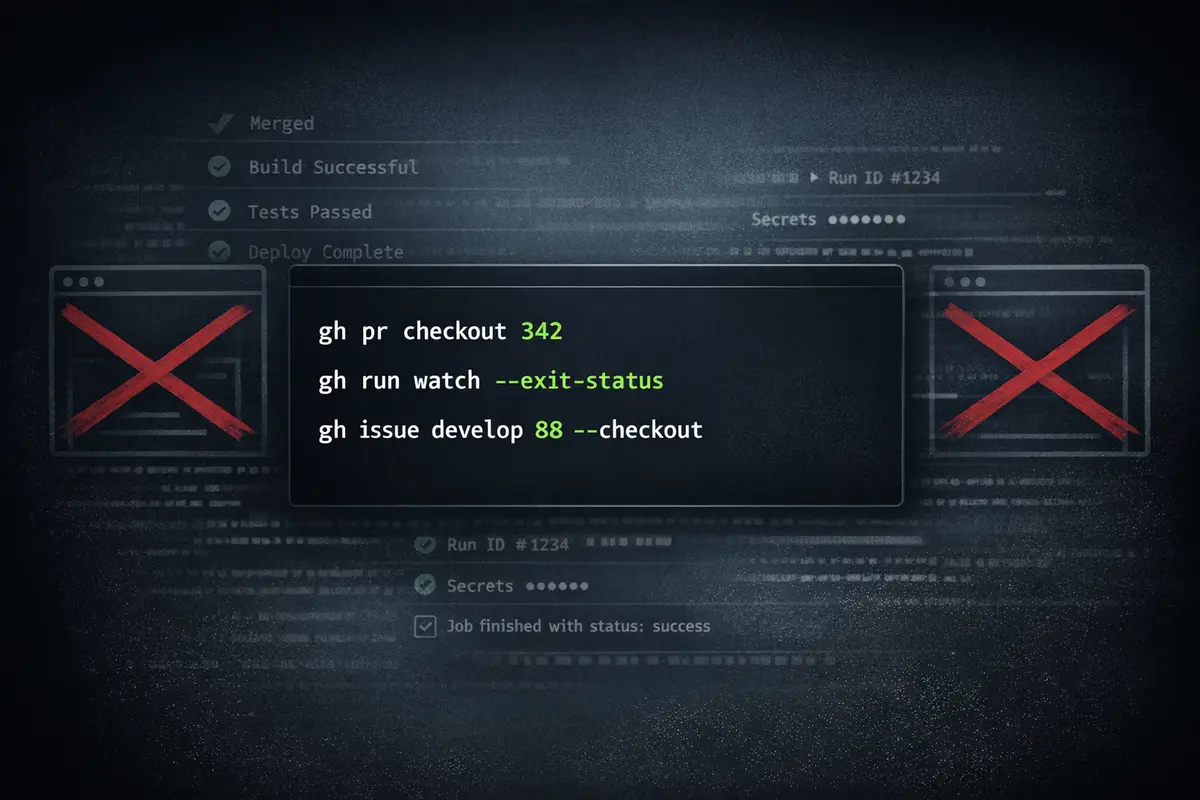
GitHub CLI Power User: 10 `gh` Commands That Replace Browser Tabs
The gh CLI covers PR reviews, workflow monitoring, secret management, and issue branching entirely from the terminal - here are the 10 commands that eliminate the browser tabs most developers still have open.
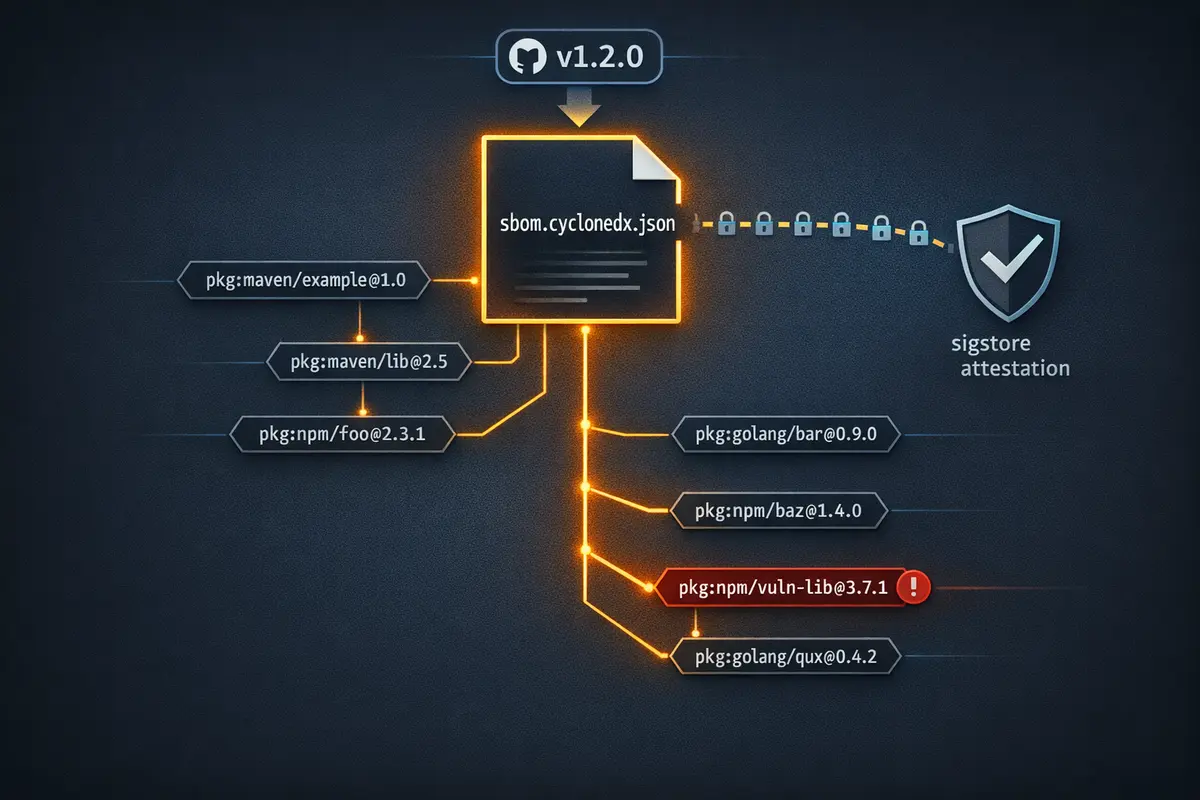
Generating and Using SBOMs with GitHub Actions
GitHub Actions makes generating a cryptographically attested, queryable CycloneDX SBOM on every release straightforward - here's the complete workflow and why the SBOM is a debugging tool as much as a compliance artifact.
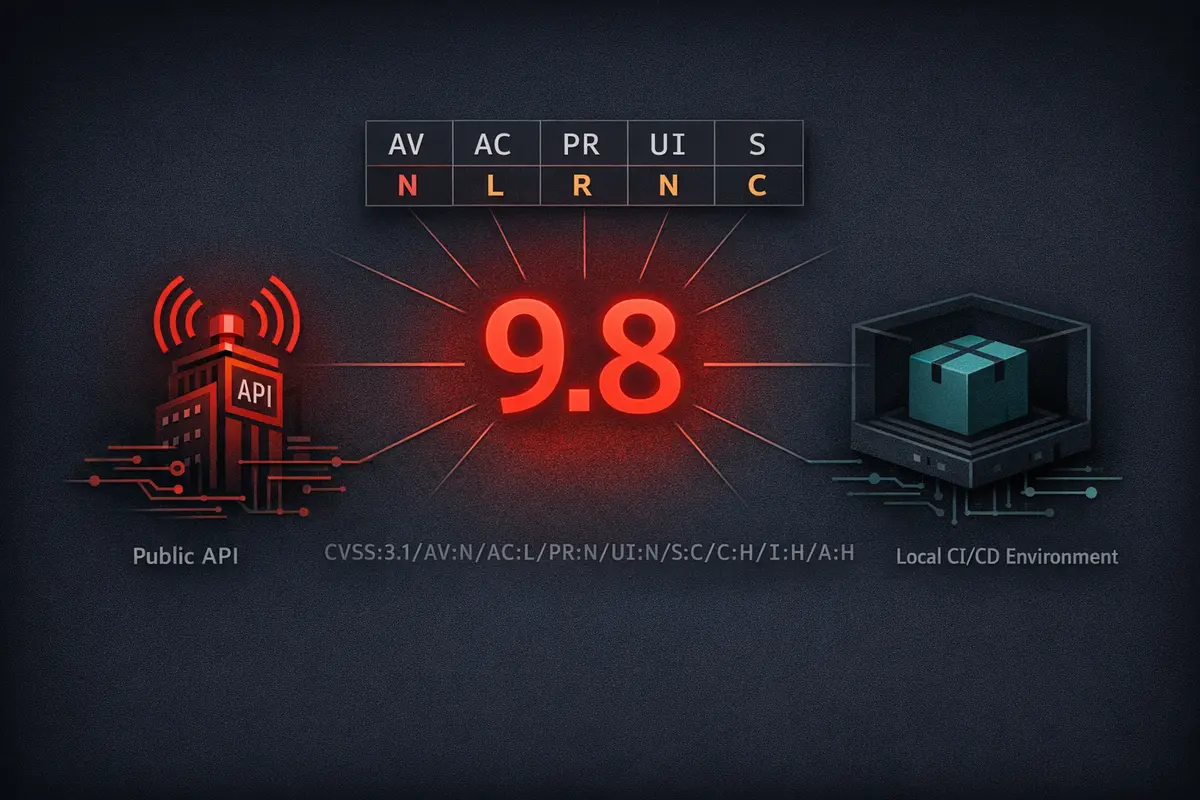
Understanding CVSS Scores: A Practical Guide for Developers
CVSS scores tell you theoretical worst-case severity, not actual risk to your application - here's how to read the vector string and triage accurately instead of panic-patching.
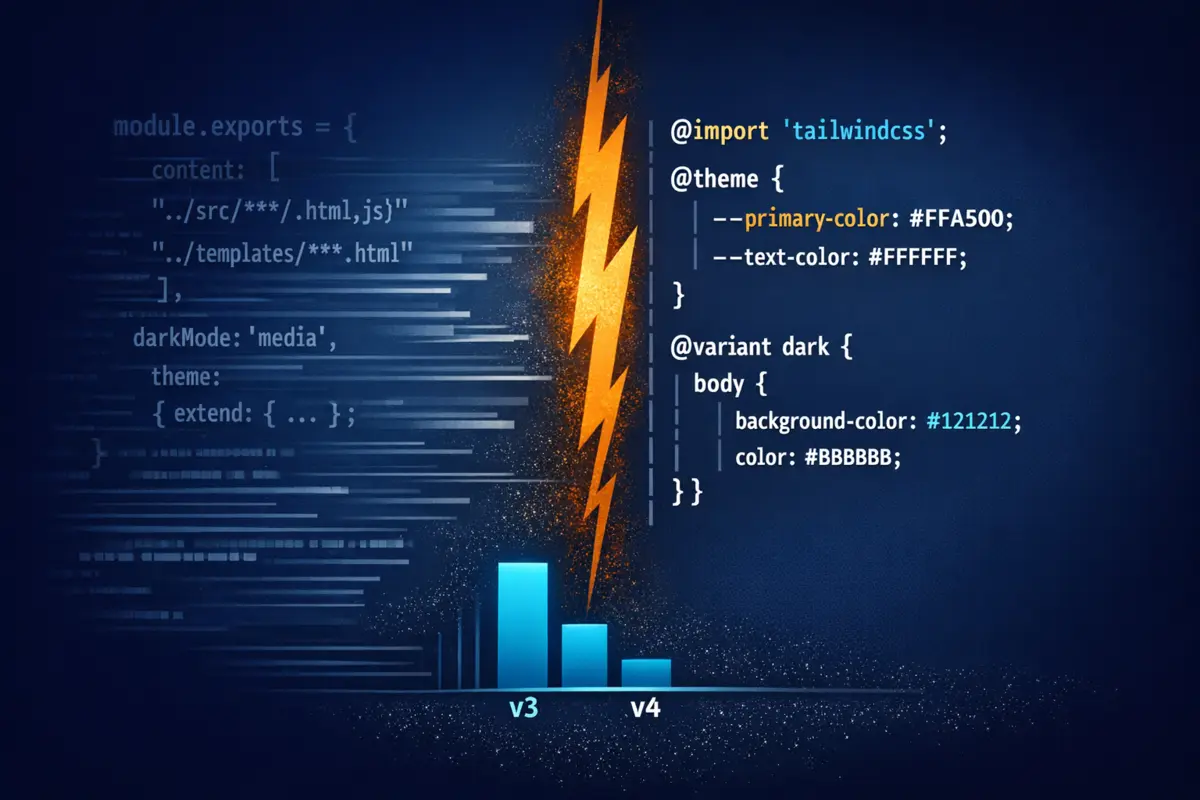
Tailwind CSS v4: What Actually Changed and How to Migrate
Tailwind CSS v4 ships a Rust-powered engine and CSS-native configuration that replaces tailwind.config.js - this post walks through migrating this blog's actual v3 config, and flags the three breaking changes most likely to catch you off-guard.
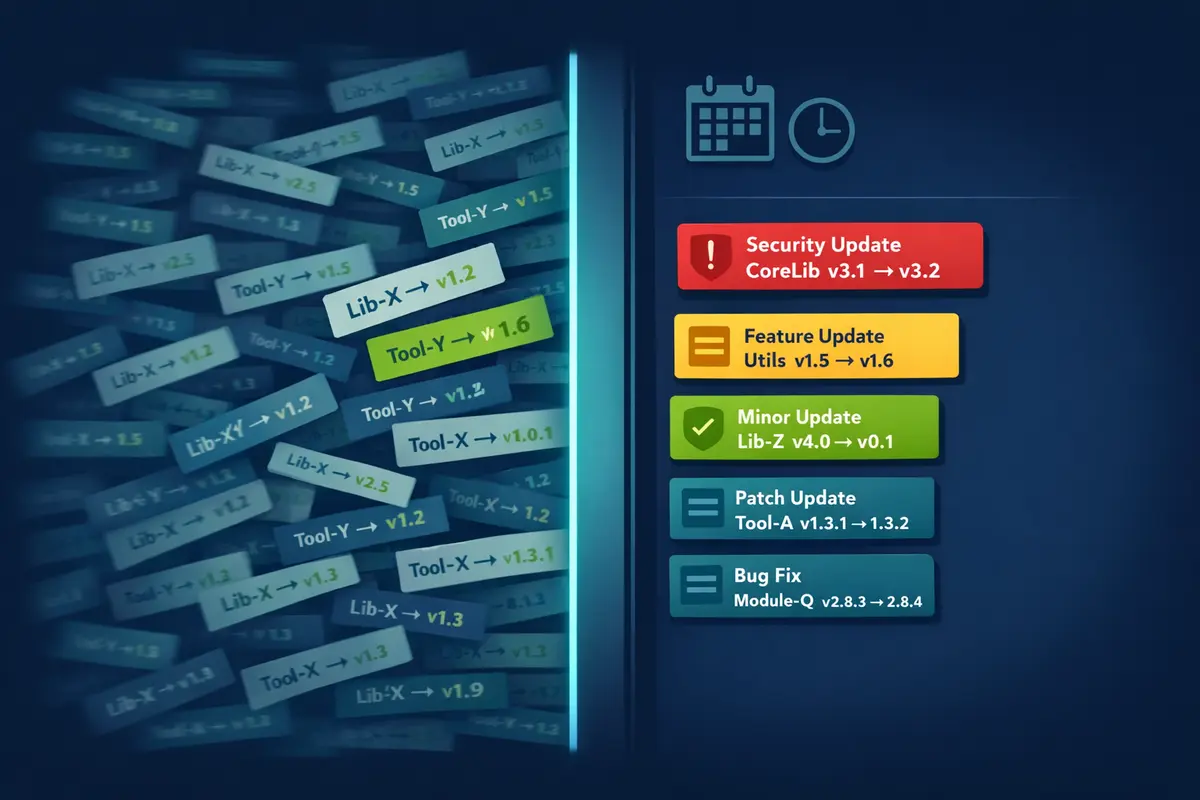
Dependabot Advanced: Getting Past the Noise
Default Dependabot floods teams with low-signal PRs until they stop merging them - here's how to tune grouping, scheduling, and auto-merge so dependency updates actually get reviewed.
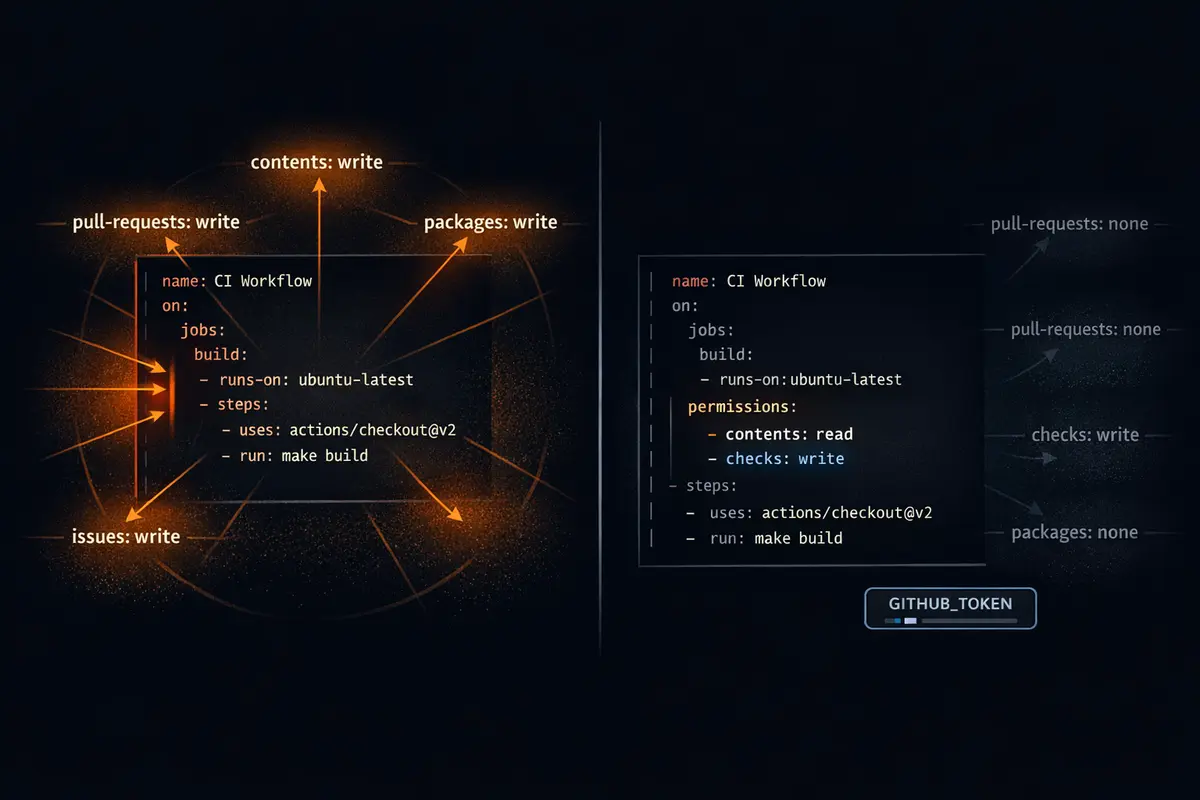
The GitHub Actions `permissions` Block: Principle of Least Privilege for Workflows
GitHub Actions workflows run with write access to almost every repo scope by default - the permissions block is three lines of YAML that closes that blast radius, and most workflows aren't using it.
Trunk-Based Development in Practice: What They Don't Tell You
Trunk-based development promises elite software delivery performance, but most adoption attempts fail on unspoken prerequisites - feature flags, expand/contract migrations, and a CI pipeline that earns trust.
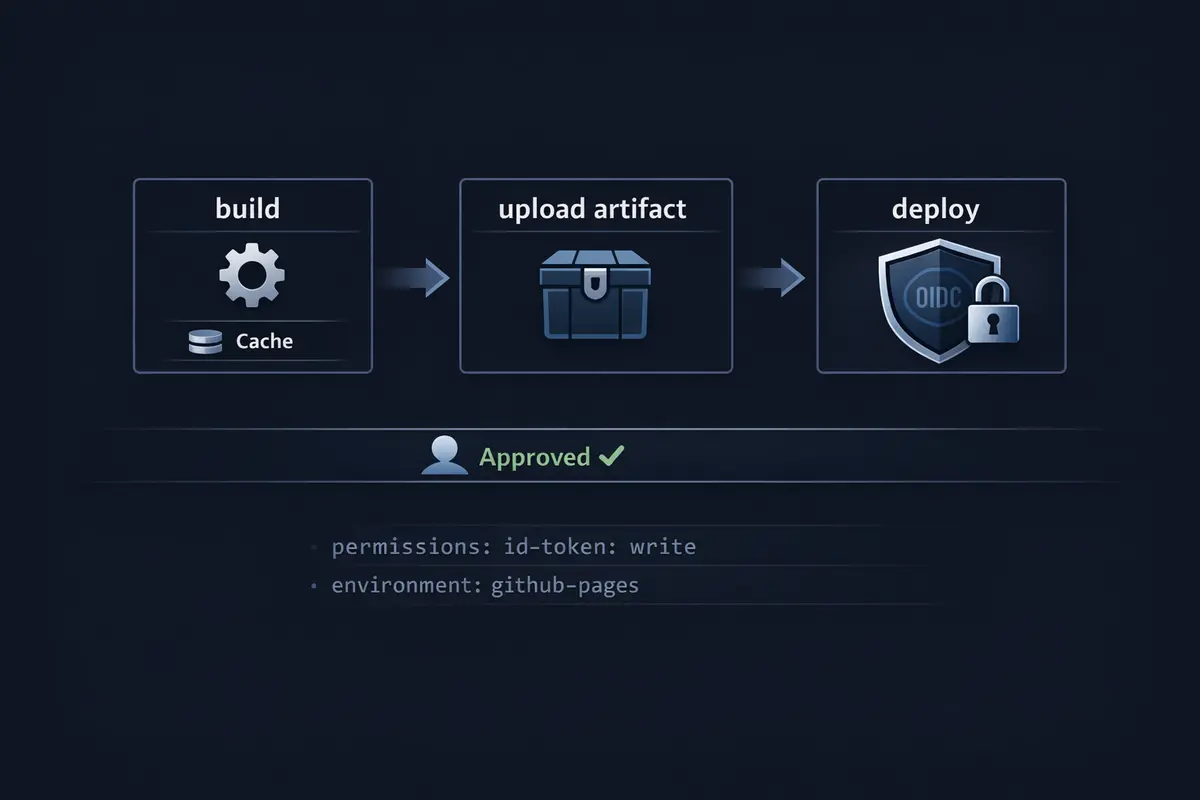
Deploying to GitHub Pages with GitHub Actions: Beyond the Defaults
The default GitHub Pages workflow skips caching, leaks artifacts, and has no deployment gate - this post rebuilds it from scratch with OIDC authentication, npm caching, and a reviewer-gated GitHub Environment.
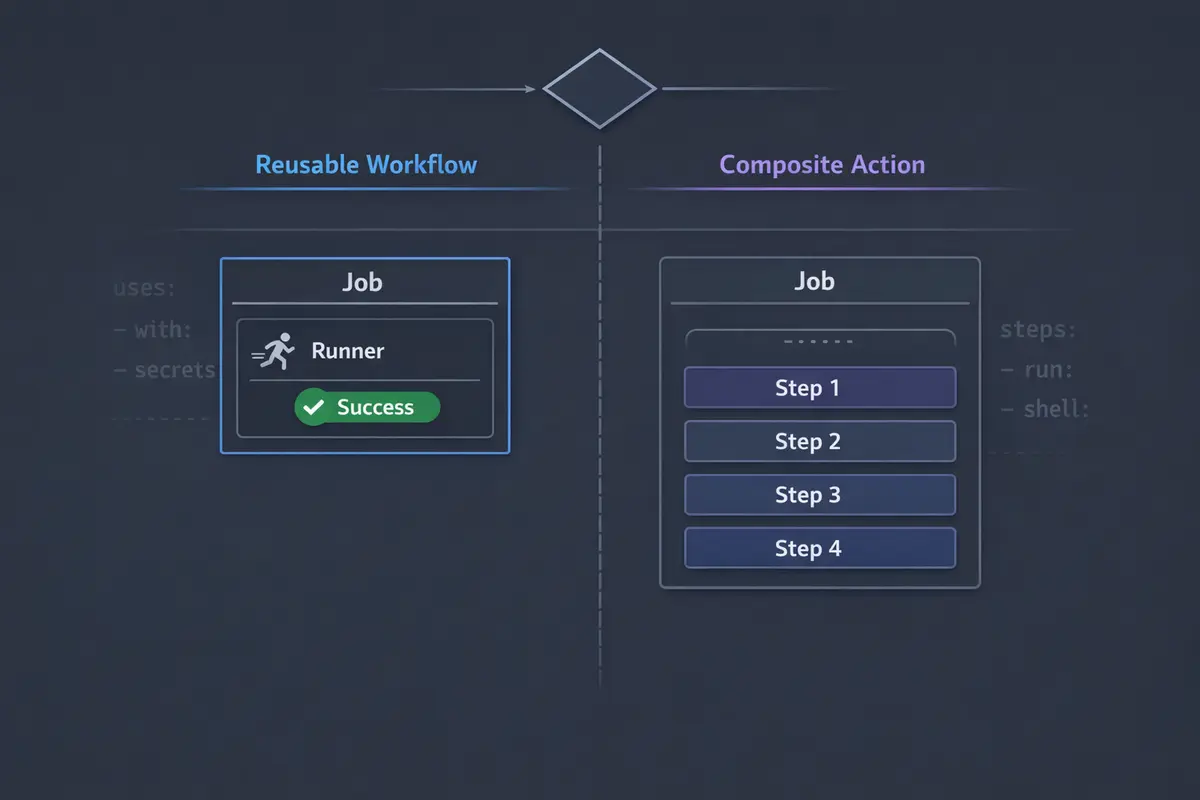
GitHub Actions: Reusable Workflows vs. Composite Actions - Know the Difference
Reusable workflows and composite actions solve different problems - understand the secret-passing rules, matrix scoping, and status-check semantics before you pick one.
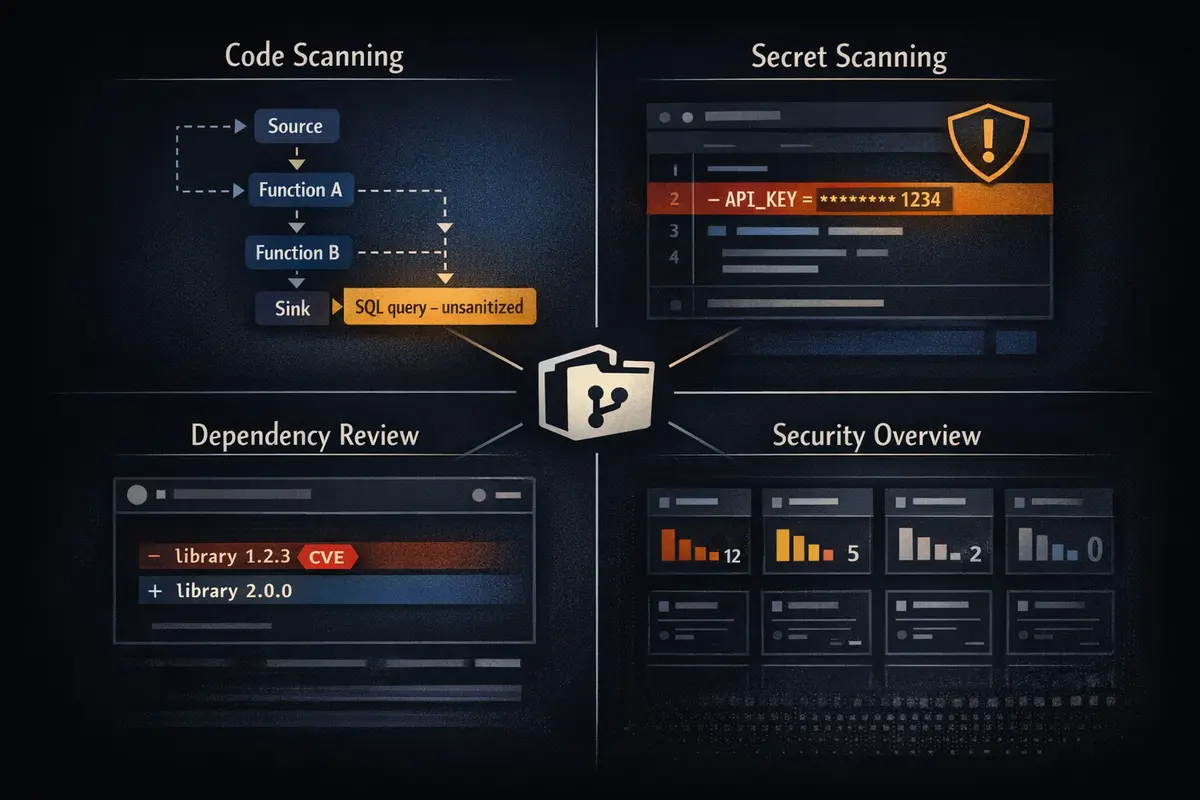
GitHub Advanced Security: What You Get and How to Use It
GitHub Advanced Security provides integrated tools like secret scanning, dependency review, and security dashboards to help DevSecOps teams embed proactive security checks into their development and CI/CD workflows.
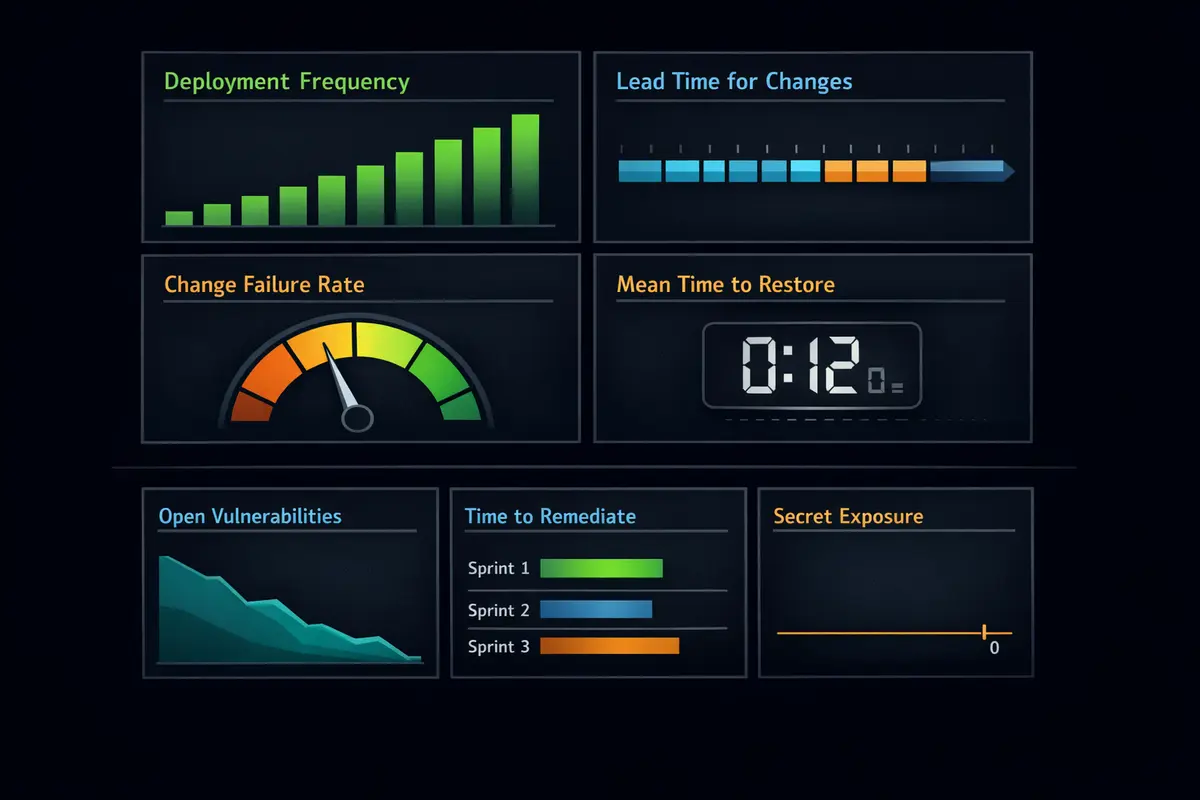
DevSecOps Metrics That Matter: What to Measure, How to Track It in GitHub, and Why It Matters
Learn the essential DevSecOps metrics, how to track them using GitHub APIs and workflows, and why they matter for balancing speed, security, and reliability.
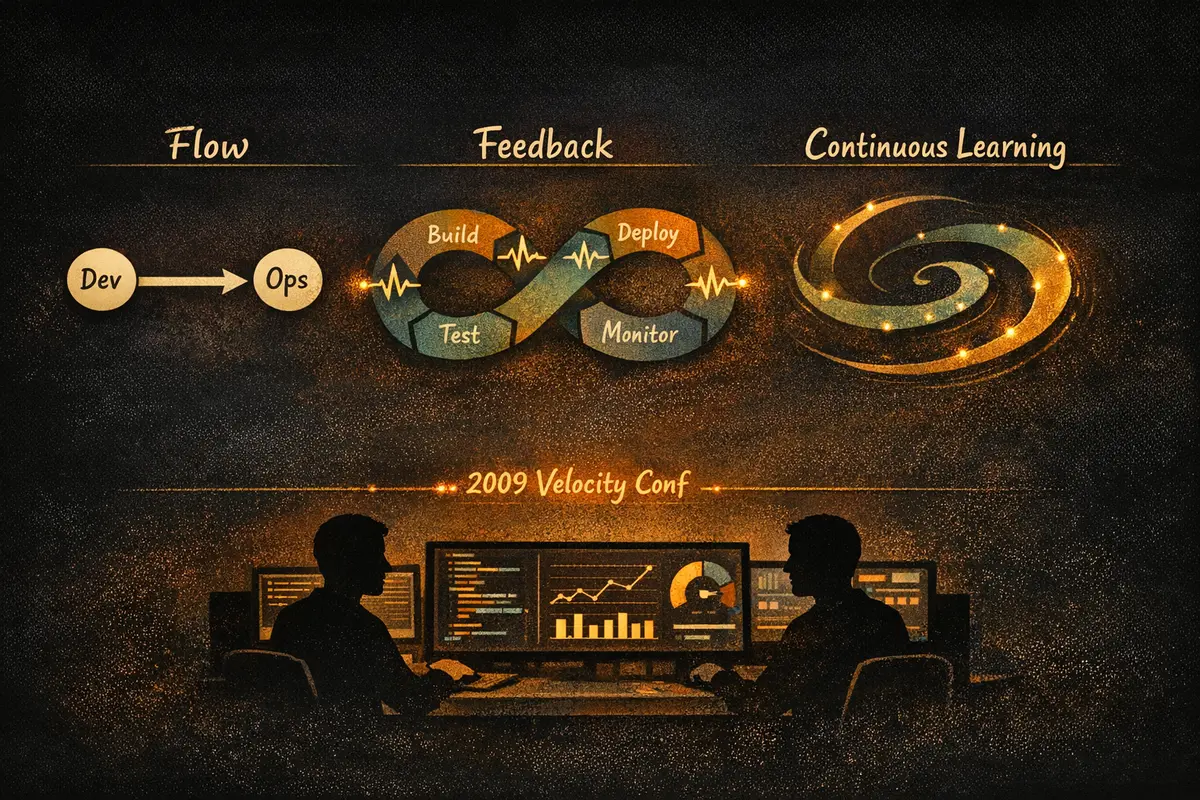
DevOps Culture: What It Is, Why It Exists, and Why It Matters
DevOps culture prioritizes collaboration and shared responsibility over tools and automation. Learn why cultural transformation is essential for faster delivery, better quality, and sustainable software development practices.
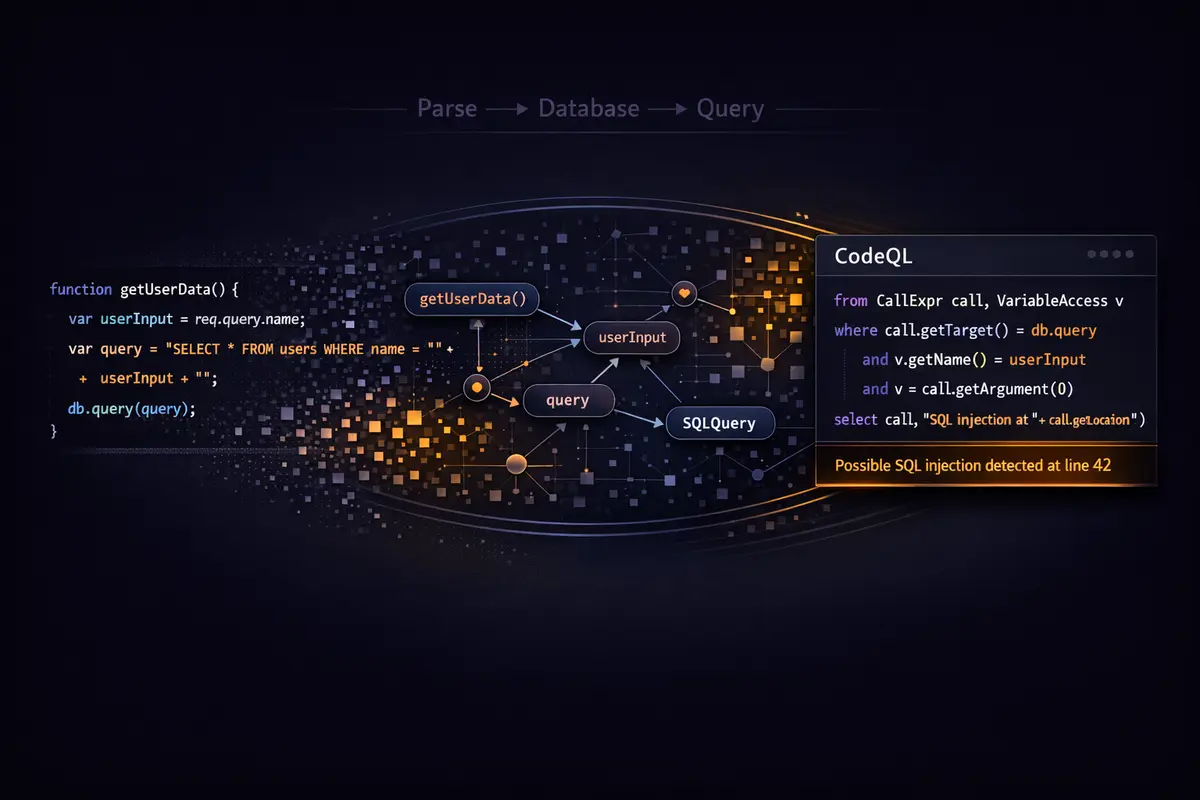
CodeQL Deep Dive: Static Analysis for DevSecOps Engineers
Master CodeQL's query-based static analysis by treating your codebase as a database. Learn to write custom queries, integrate with CI/CD pipelines, and detect vulnerabilities with precision.
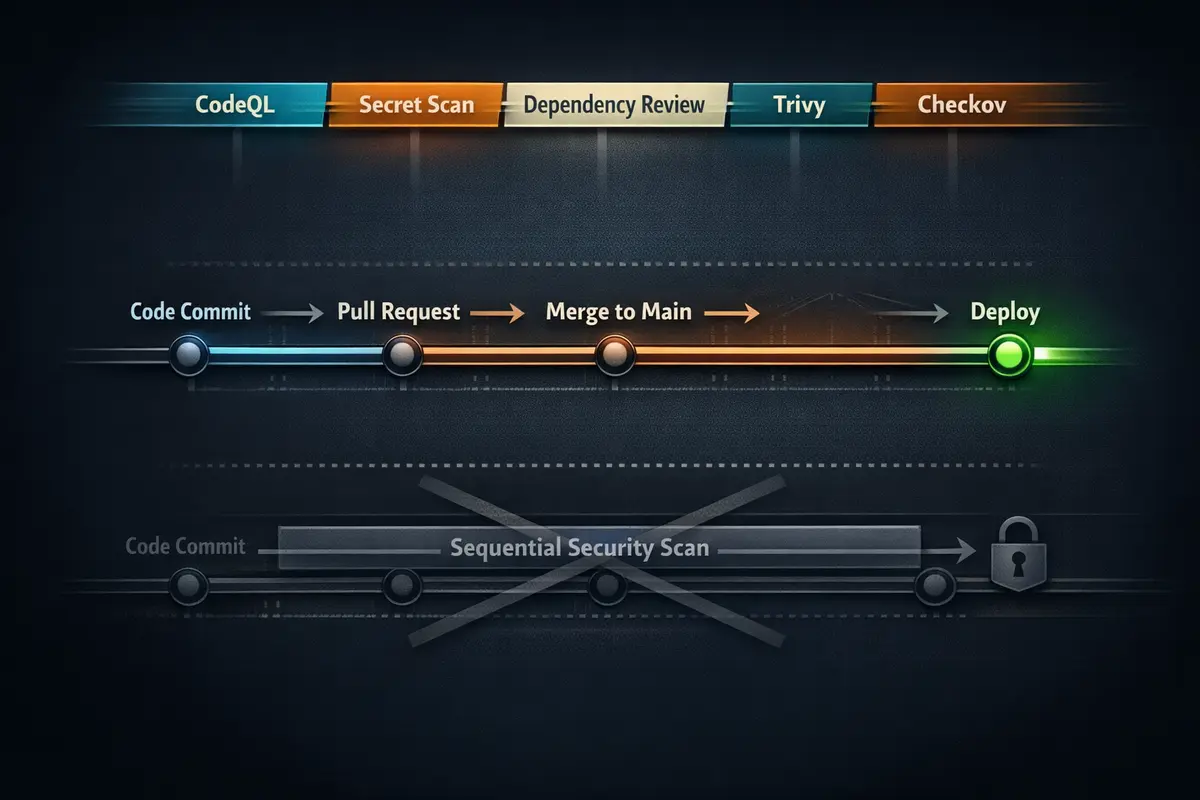
Shift Left Without Slowing Down: DevSecOps Pipeline Design
Learn how to securely manage secrets on GitHub using secret scanning, environment variables, and best practices to prevent credential leaks and security breaches.
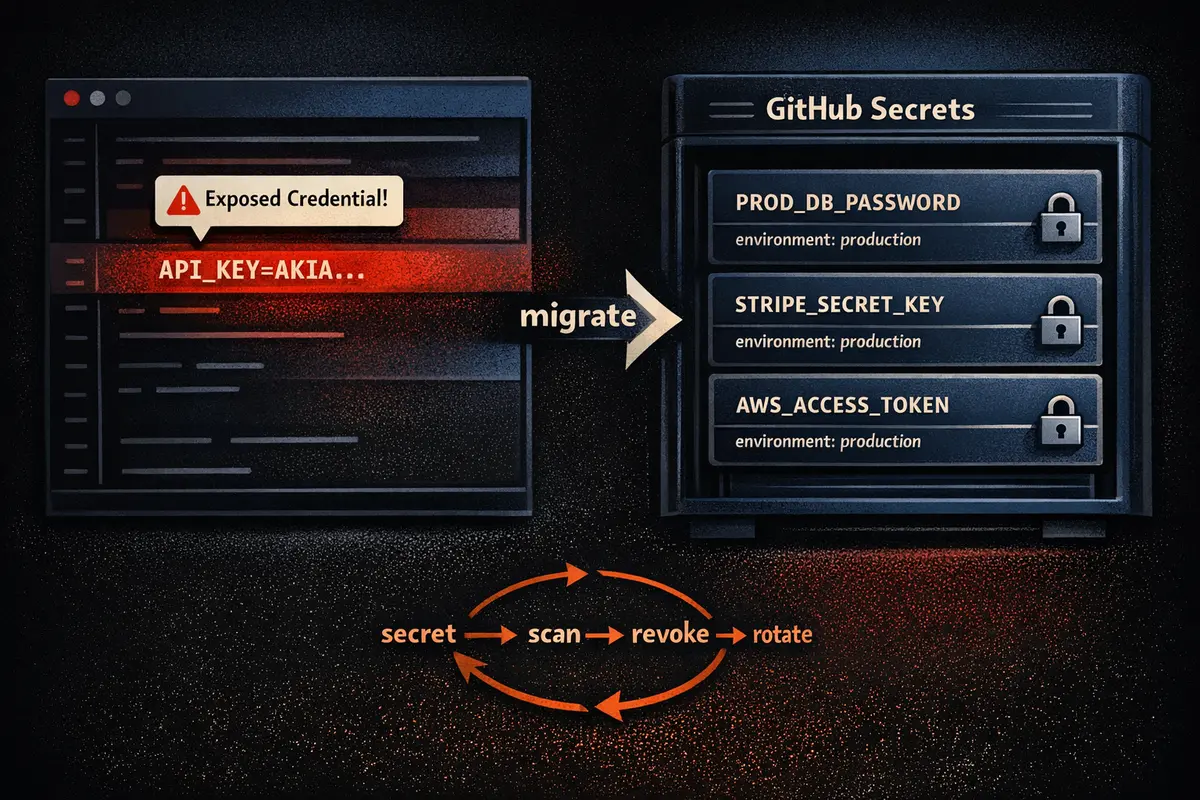
Secrets Management on GitHub: Best Practices and Pitfalls
Learn how to securely manage secrets on GitHub using secret scanning, environment variables, and best practices to prevent credential leaks and security breaches.
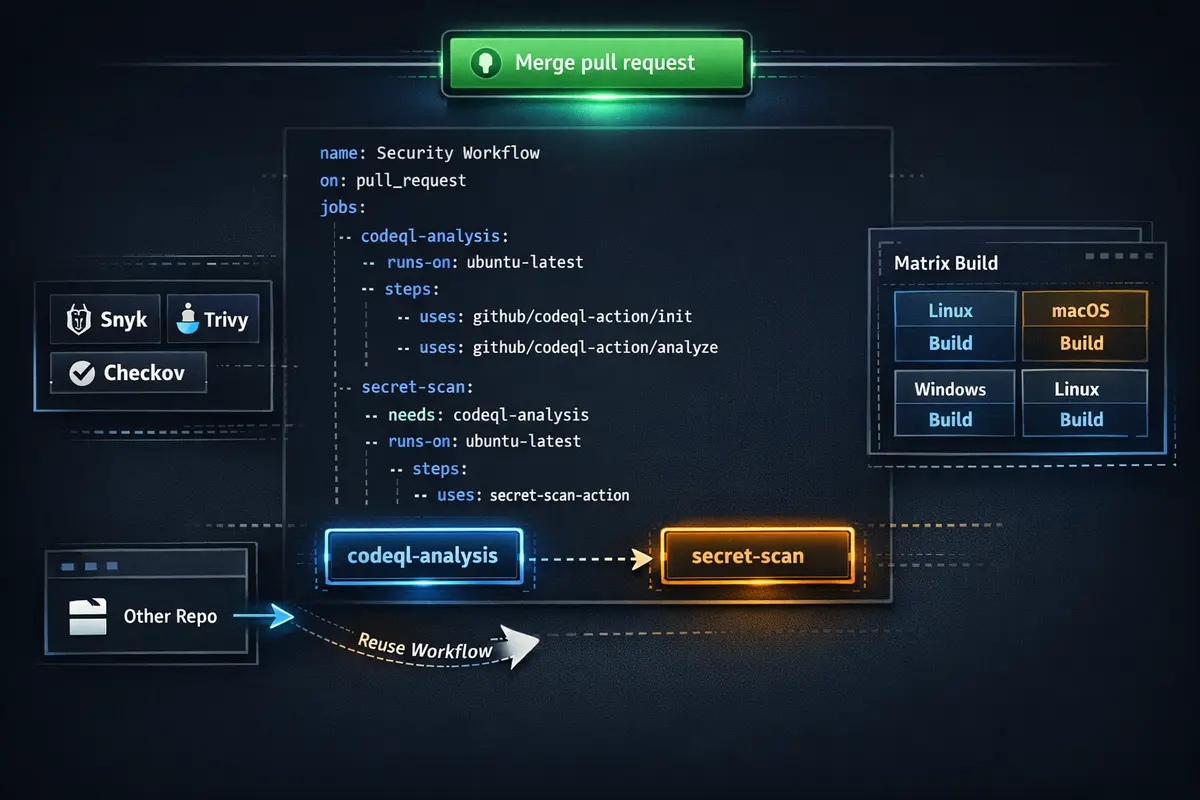
Security as Code with GitHub Actions: Automating DevSecOps
Learn how to implement Security as Code using GitHub Actions. Explore reusable workflows, Marketplace integrations, matrix builds, and best practices for embedding security into CI/CD pipelines.
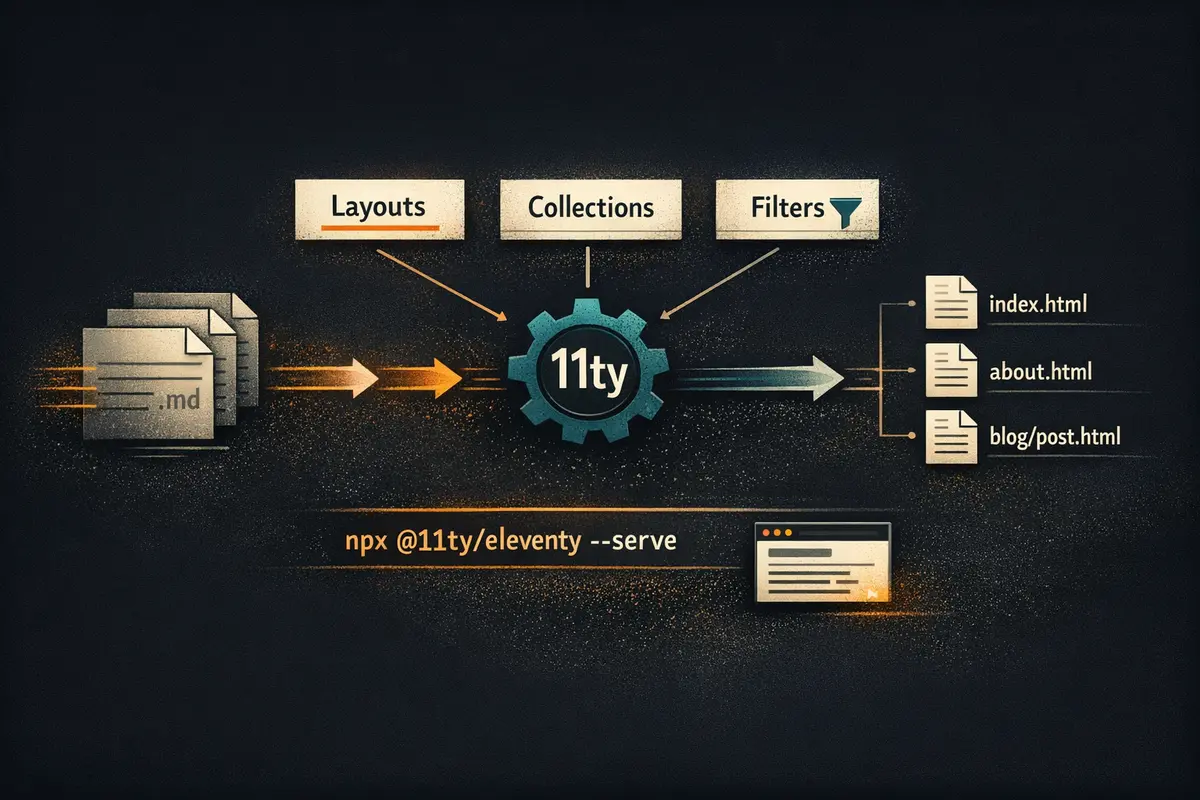
Getting Started with Eleventy
Eleventy is a simpler static site generator. Learn why it's great for building fast, modern websites and how to get started with your first project.
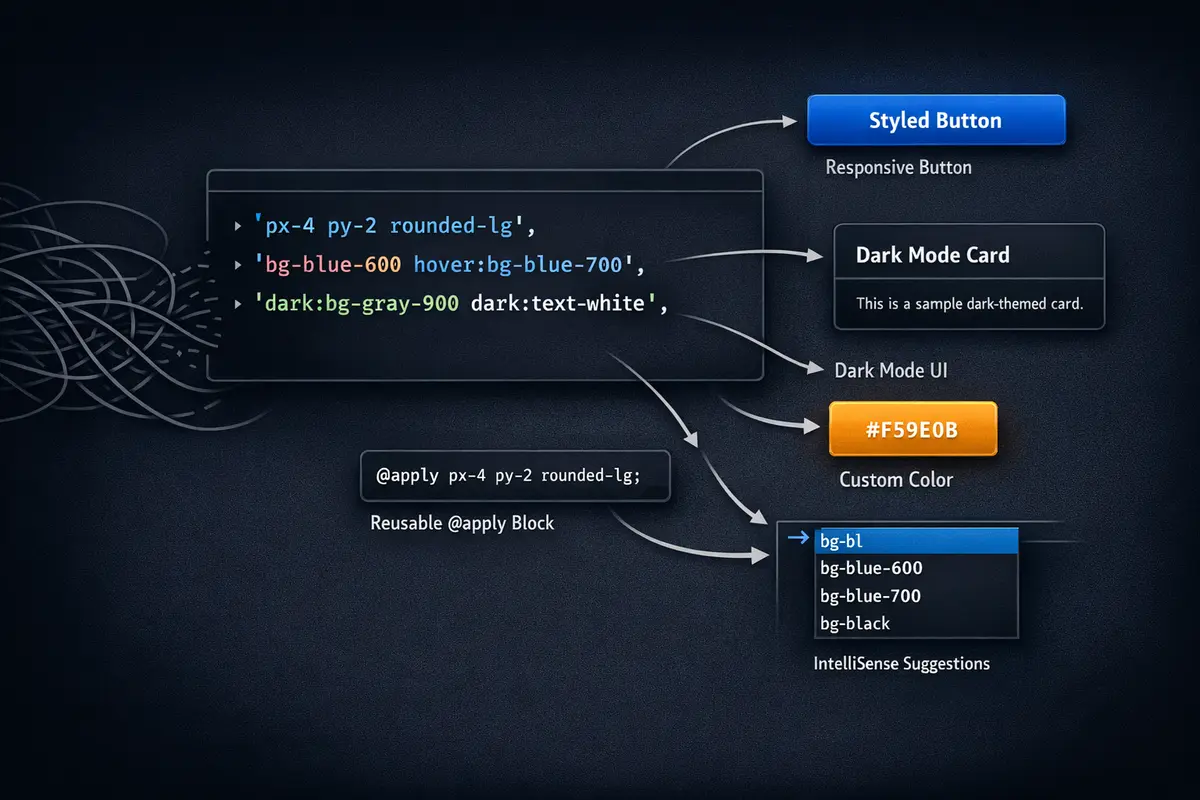
5 Tailwind CSS Tips for Better Productivity
Boost your productivity with these practical Tailwind CSS tips and tricks. Learn how to write cleaner, more maintainable utility-first CSS.
Why GitHub is the DevSecOps Platform of Choice
Why GitHub is a strong platform choice for DevSecOps teams - built-in automation, native security tooling, and auditability.